Running External Network Pentest by Strobes AI
6 min readEdit
On this page⌄
- Overview
- Why Is It Needed?
- Benefits
- Available Assessment Templates
- External Network Pentest - Fast
- External Network Pentest - Standard
- External Network Pentest - Deep
- Which Template Should I Choose?
- Prerequisites
- Accessing the External Network Pentest Template
- Review the template details
- Configuring the Target Scope
- Step 1: Provide a Workspace Name
- Step 2: Enter the Target IP or Range
- Step 3: Add Exclusions (Optional)
- Step 4: Select Credentials (Optional)
- Step 5: Add Other Credentials (Optional)
- Step 6: Add Custom Instructions (Optional but highly recommended)
- Proceeding to Configuration
- Step 7: Select an AI Model
- Step 8: Review the Execution Shell and Browser
- Step 9: Select the Execution Mode
- Step 10: Review the Schedule
- Step 11: Continue to Review and Launch
- Step 12: Review and Launch the Workspace
- Tips
Overview
An External Network Pentest in Strobes helps identify security vulnerabilities in the internet-facing IPs and network ranges of your organization. An AI agent discovers live hosts and services, assesses them, correlates them with known vulnerabilities, verifies what it finds, and provides evidence and remediation guidance to help teams address the risks.
Why Is It Needed?
Your external network is the first thing an attacker sees. Open ports, exposed services, and outdated software can give attackers an easy way in. Testing your public IPs regularly helps you find and fix these exposures before they are exploited. Because the agent verifies findings before reporting them, your team spends time on genuine issues instead of noise.
Benefits
- On-Demand Testing: Run a pentest whenever you need it, without waiting for a manual engagement.
- Verified Findings: Focus on confirmed vulnerabilities with severity, evidence, and remediation guidance.
- Nothing to Install: Strobes scans your public IPs or CIDR ranges from its cloud sandbox.
- Findings in Strobes: Findings are created and linked to assets automatically.
- Report Included: A comprehensive report is generated at the end of the workflow.
- Full Control: Pause, resume, or step in at any phase.
Available Assessment Templates
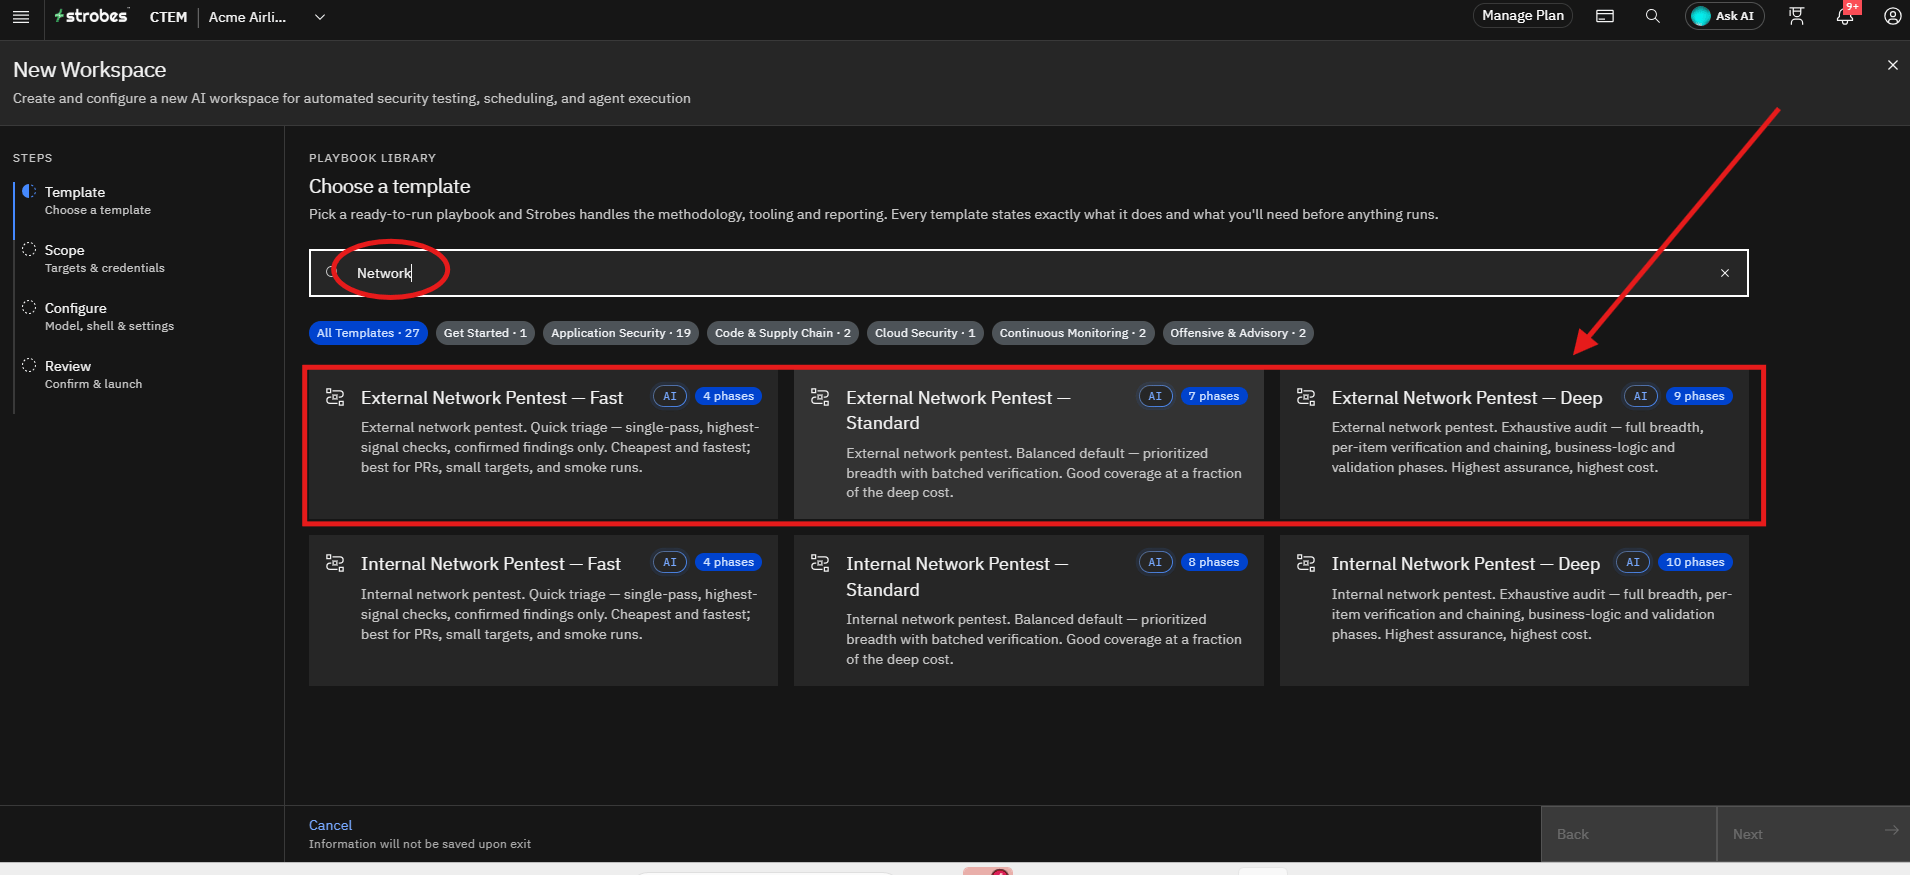
Strobes offers three External Network Pentest templates, Fast, Standard, and Deep, so you can choose the level of security analysis that best suits your environment.
External Network Pentest - Fast
A quick triage focused on the highest-signal issues.
- Runs 4 phases in a single pass.
- Reports confirmed findings only, and generates a report.
- Cheapest and fastest option.
Best for: Pull requests, small targets, and smoke runs.
External Network Pentest - Standard
A balanced pentest that suits most environments.
- Runs 7 phases.
- Prioritizes breadth with batched verification.
- Gives good coverage at a fraction of the Deep cost.
Best for: Regular security testing of most external networks.
External Network Pentest - Deep
The most complete pentest, designed for the highest level of assurance.
- Runs 9 phases: Scope, OSINT & Target Expansion; Host Discovery & Service Scan; Attack Surface Mapping & Prioritization; Service Assessment; Threat Intelligence & CVE Correlation; Exploitation; Lateral Movement & Chaining; Finding Validation; and Reporting.
- Performs per-item verification and chaining, with business logic and validation phases.
- Highest assurance and highest cost.
Best for: Critical environments, networks that expose sensitive systems, and in-depth security audits.
Which Template Should I Choose?
Feature | Fast | Standard | Deep |
|---|---|---|---|
Number of Phases | 4 | 7 | 9 |
Testing Approach | Single pass, highest-signal checks | Prioritized breadth with batched verification | Exhaustive audit with per-item verification |
Review Depth | Quick | Thorough | Most complete |
Host Discovery and Service Scan | Included | Included | Included |
Attack Surface Mapping and Prioritization | Not included | Included | Included |
Threat Intelligence and CVE Correlation | Not included | Included | Included |
Exploitation and Chaining | Not included | Limited | Included, including lateral movement |
Finding Validation | Confirmed findings only | Batched verification | Per-item verification |
Run Time and Credit Usage | Lowest | Moderate | Highest |
Prerequisites
Before you start, make sure you have:
- Access to Strobes AI Workspaces in your organization.
- Enough AI credits. Each run uses AI credits. Deep uses the most, while Fast uses the least.
- The public IP addresses or CIDR ranges you want to test, such as
203.0.113.0/24or198.51.100.10. - Authorization to test the targets.
- (Optional) Any IPs or ports you want to exclude from the scope.
- (Optional) Credentials from the credential manager, if the test needs them.
Note: External Network Pentest scans public IPs or CIDR ranges from the Strobes cloud sandbox, so nothing needs to be installed in your network. To test systems behind your firewall, use the Internal Network Pentest template instead.
Accessing the External Network Pentest Template
Strobes offers different External Network Pentest templates based on the required level of security analysis. For this guide, we will use the Deep template. The steps are the same for Fast and Standard.
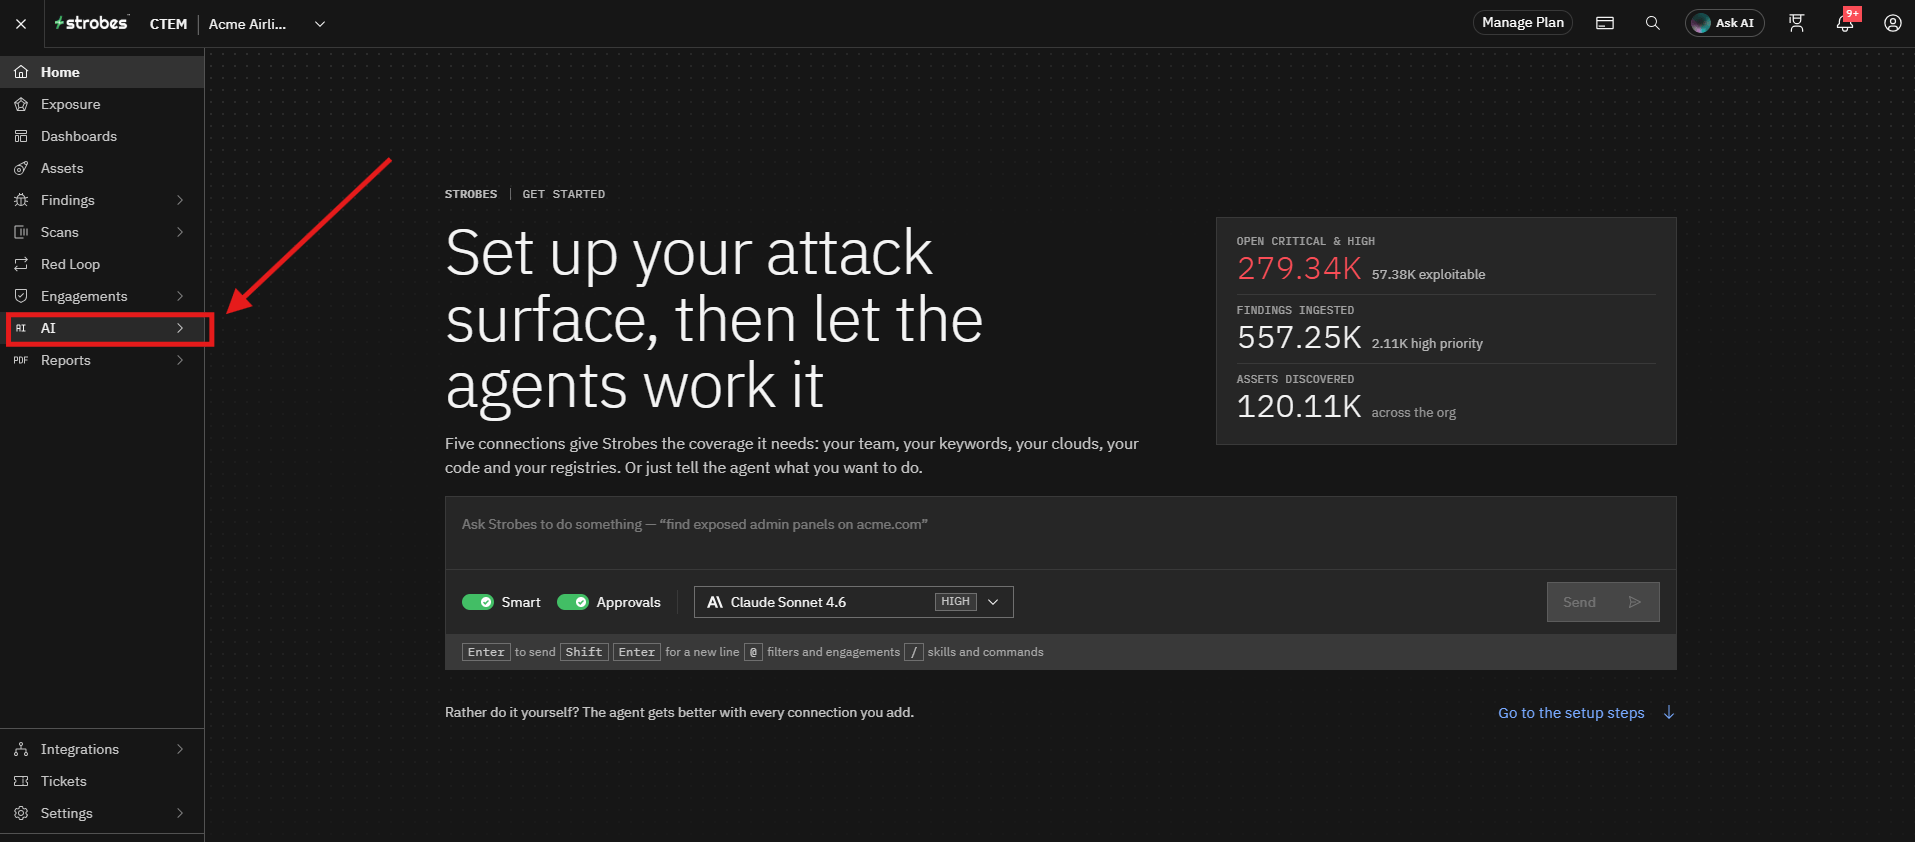
- Navigate to AI from the main navigation menu.
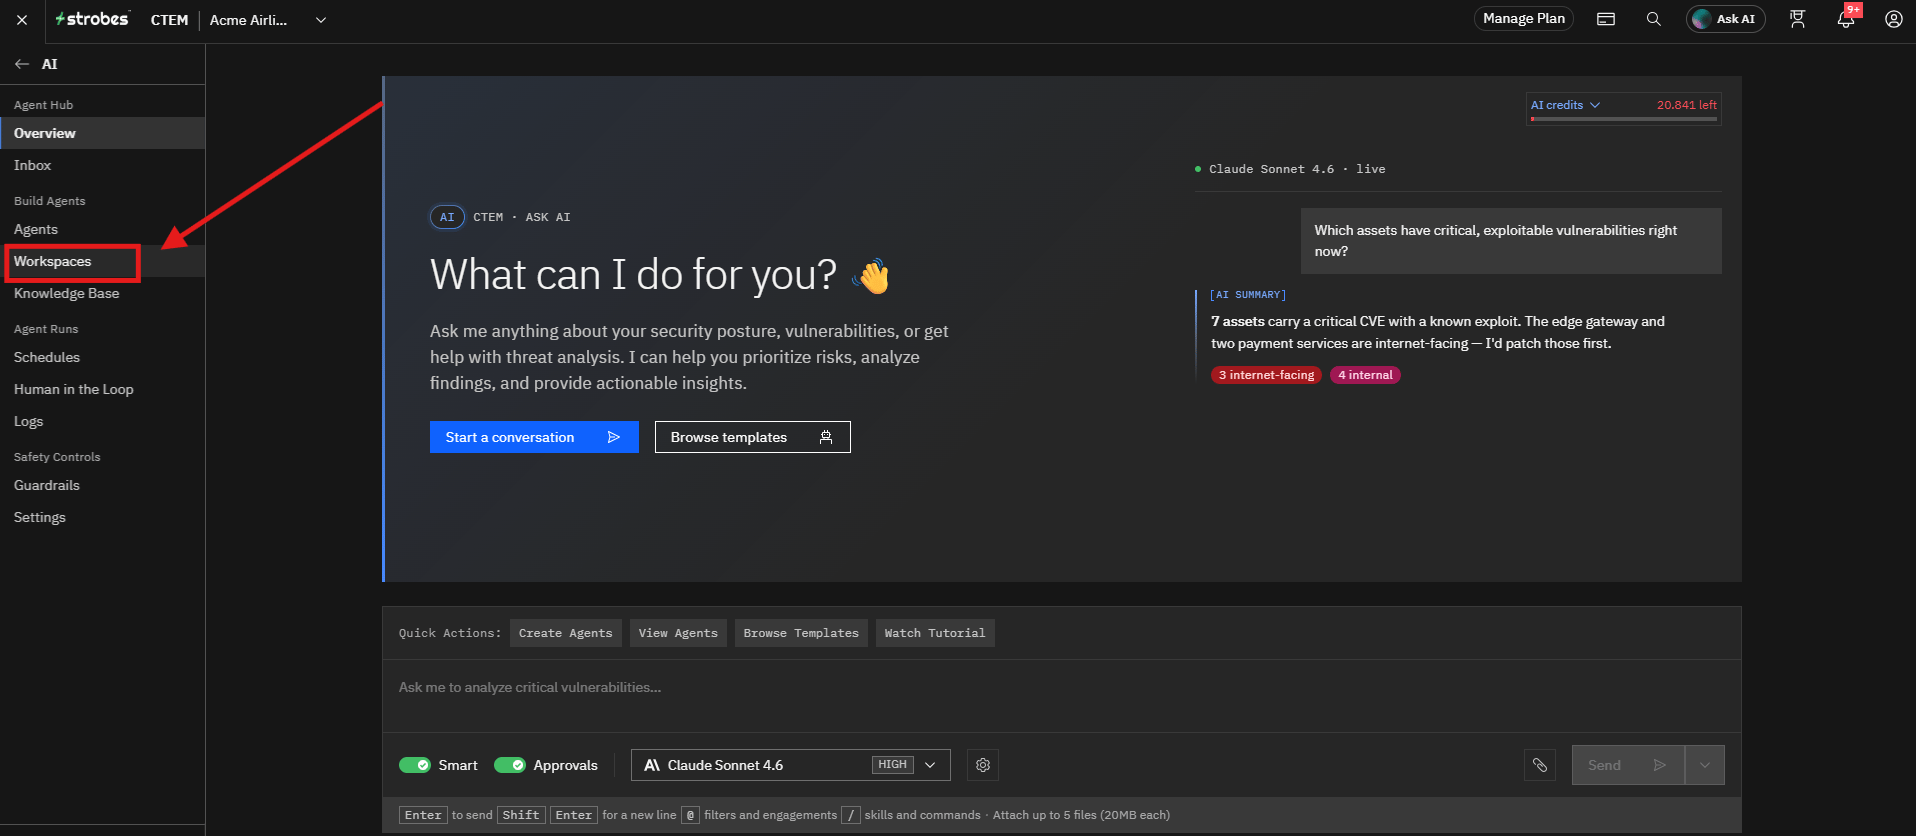
- Open the Workspaces page.
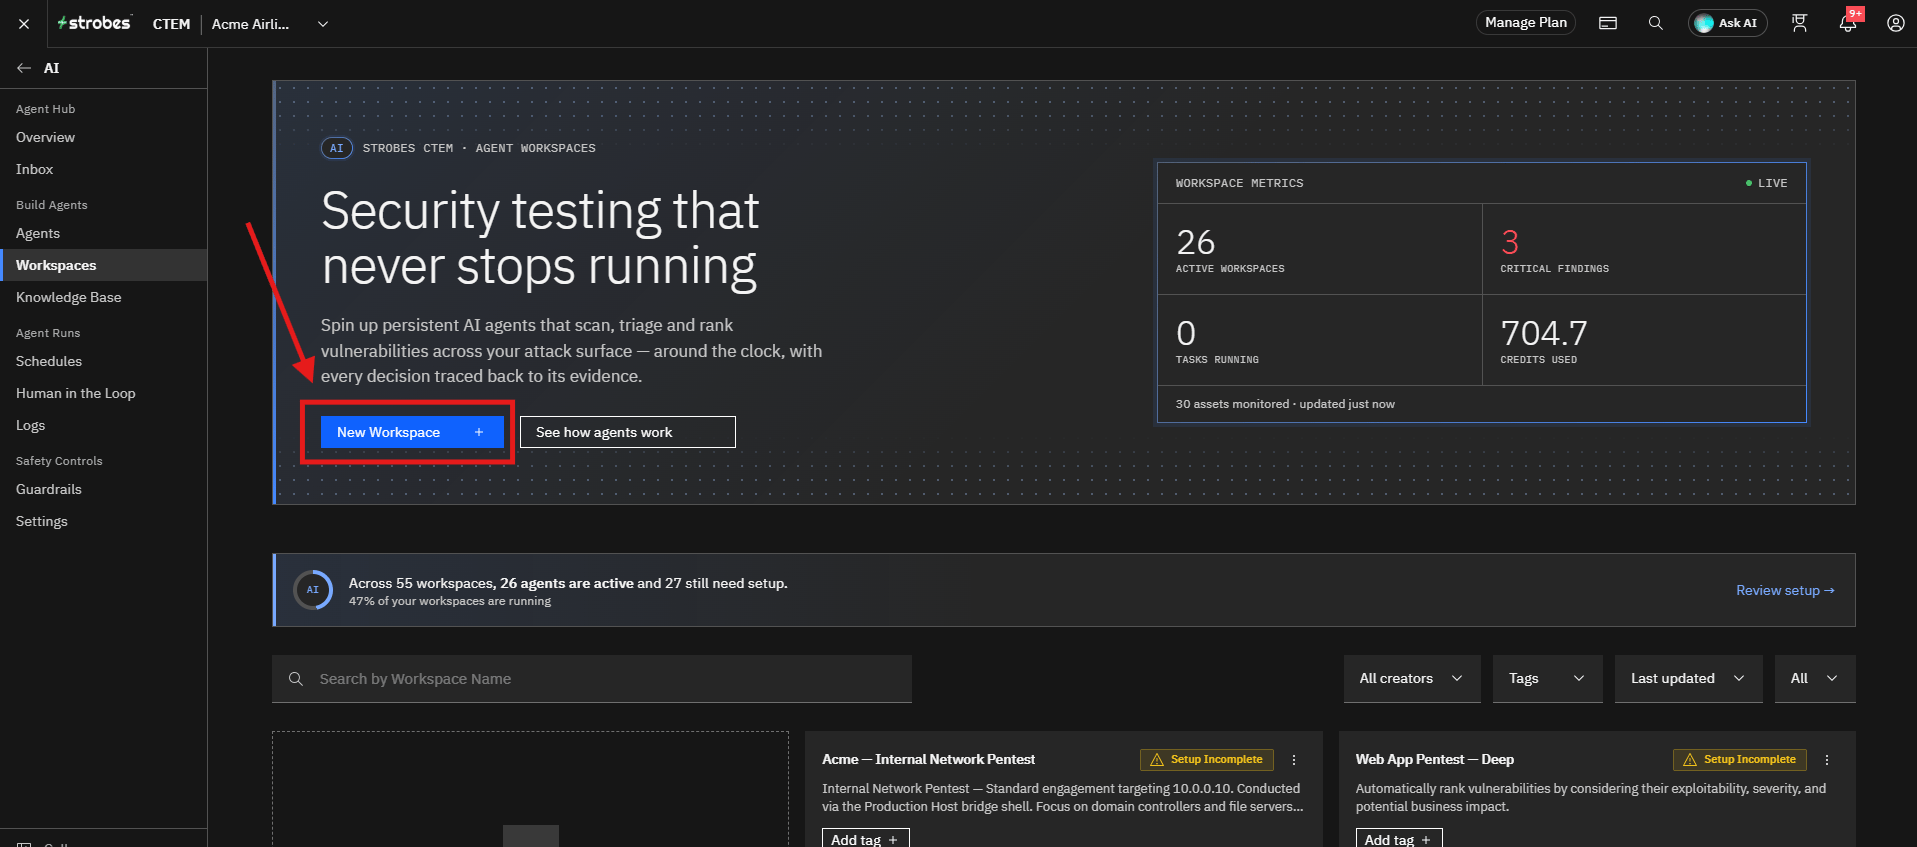
- Click New Workspace.
- In the Playbook Library, search for
networkand select the External Network Pentest template you want.
Review the template details
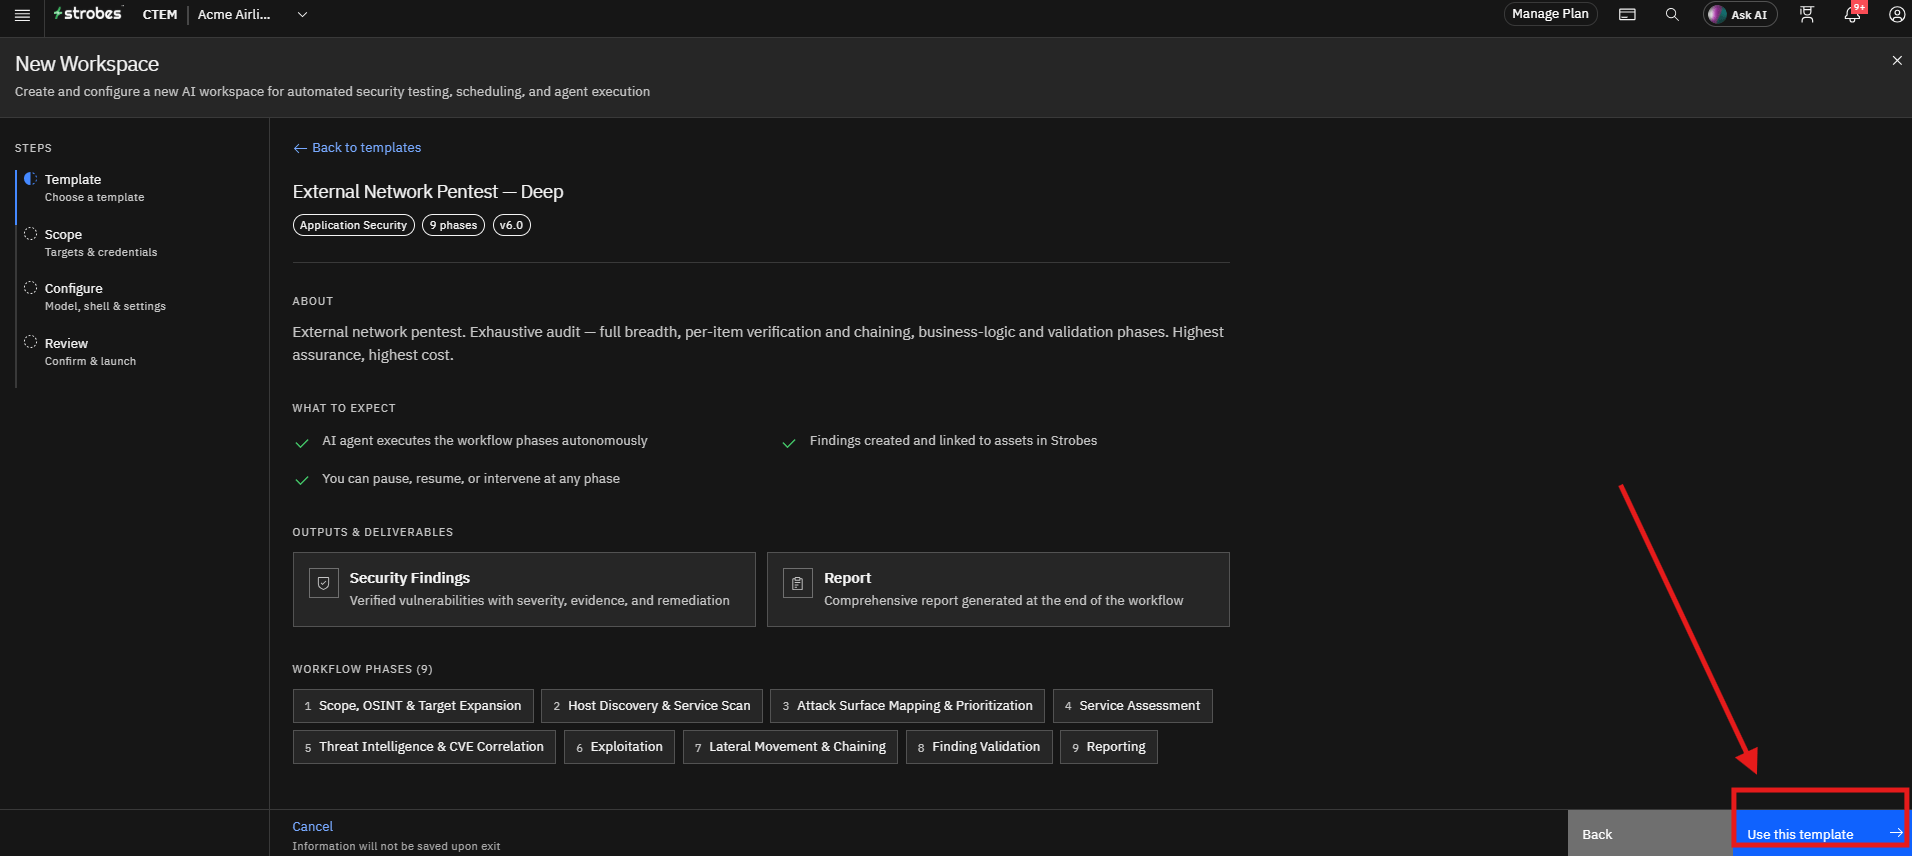
Selecting a template opens its details page, which shows:
- Tags: The category, number of phases, and version.
- About: What the template does.
- What to expect: The AI agent executes the workflow phases autonomously, findings are created and linked to assets in Strobes, and you can pause, resume, or intervene at any phase.
- Outputs & deliverables: Security Findings and a Report.
- Workflow phases: The phases the template runs, in order. For example, External Network Pentest - Deep runs 9 phases, from scope and OSINT to finding validation and reporting.
To continue, select Use this template. To choose a different template, select Back or Back to templates.
- Click Use this template.
Configuring the Target Scope
After selecting the template, the wizard automatically moves to the Scope step.
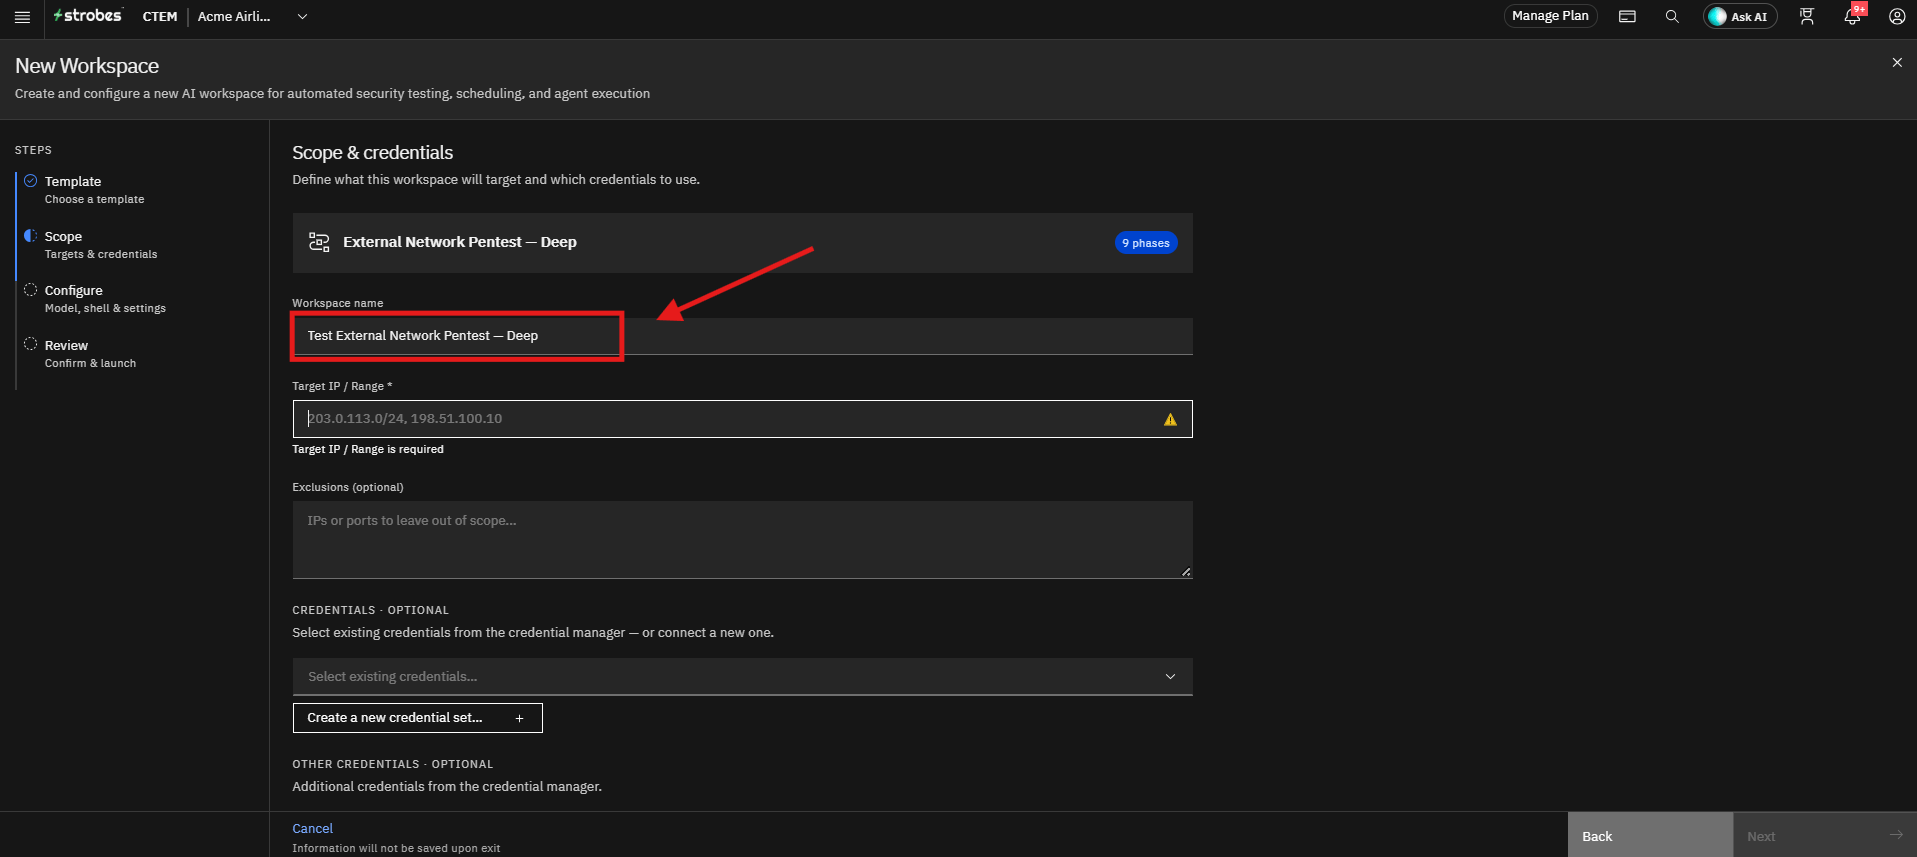
Step 1: Provide a Workspace Name
The Workspace name is pre-filled with the template name. Enter a more meaningful name for the assessment if you want, such as the name of the network or business unit.
Step 2: Enter the Target IP or Range
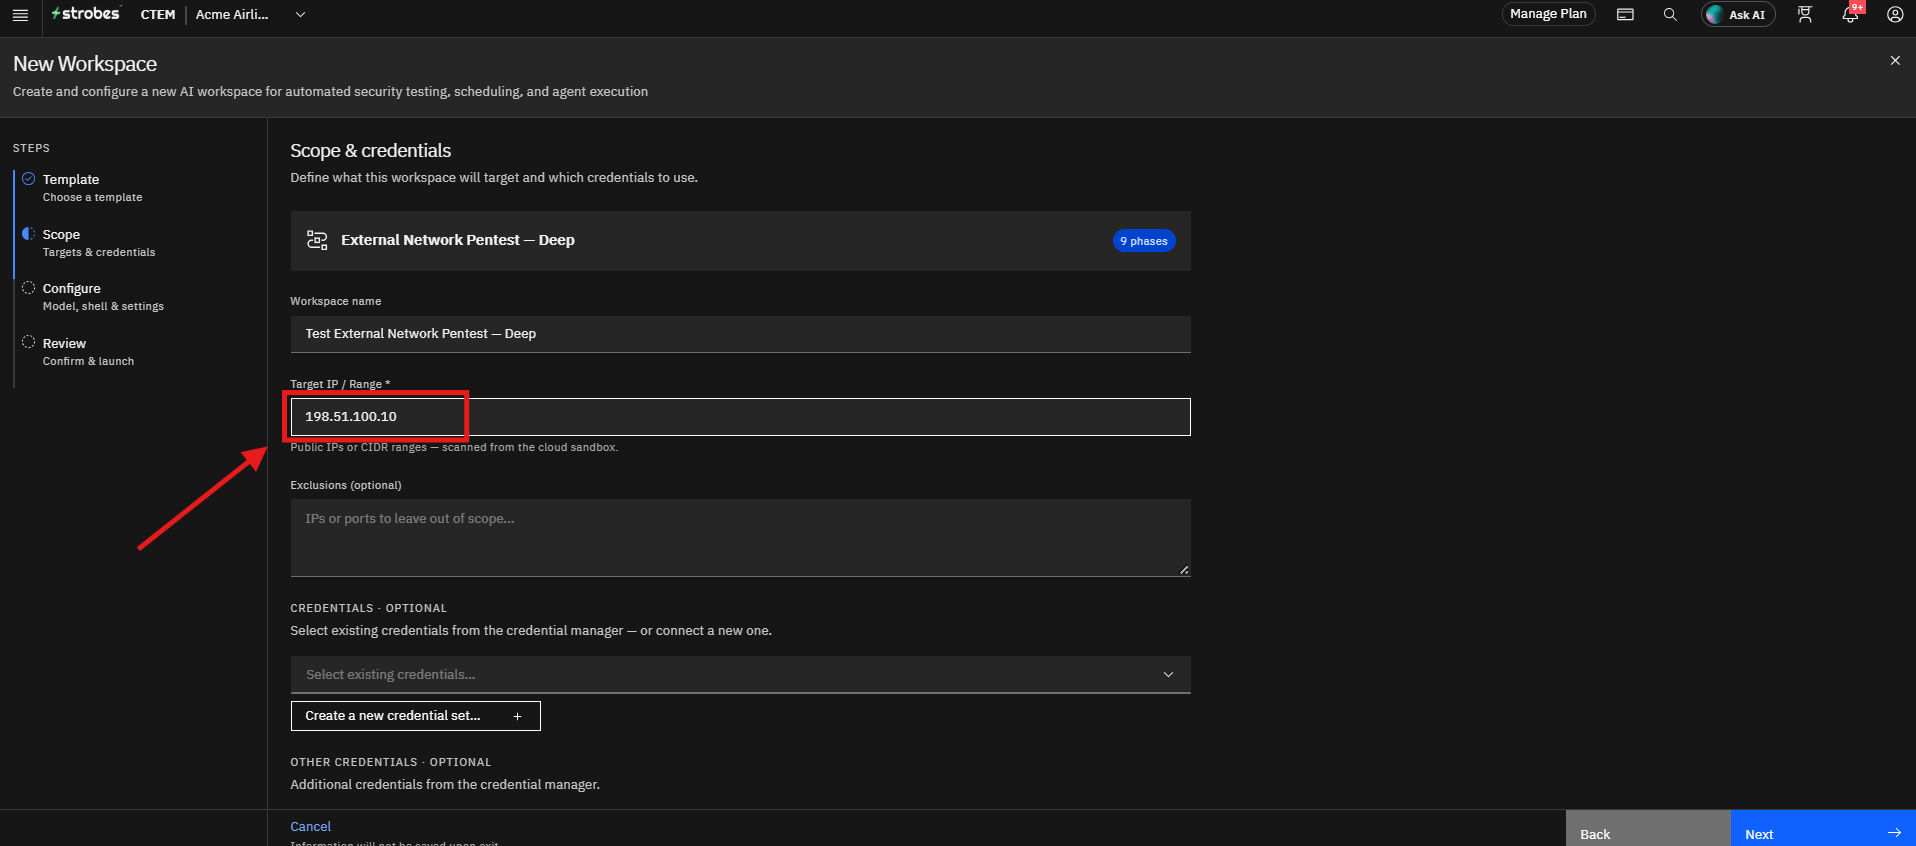
In the Target IP / Range field, enter the public IP addresses or CIDR ranges you want to test. Separate multiple entries with commas, for example 203.0.113.0/24, 198.51.100.10. Strobes scans these from its cloud sandbox.
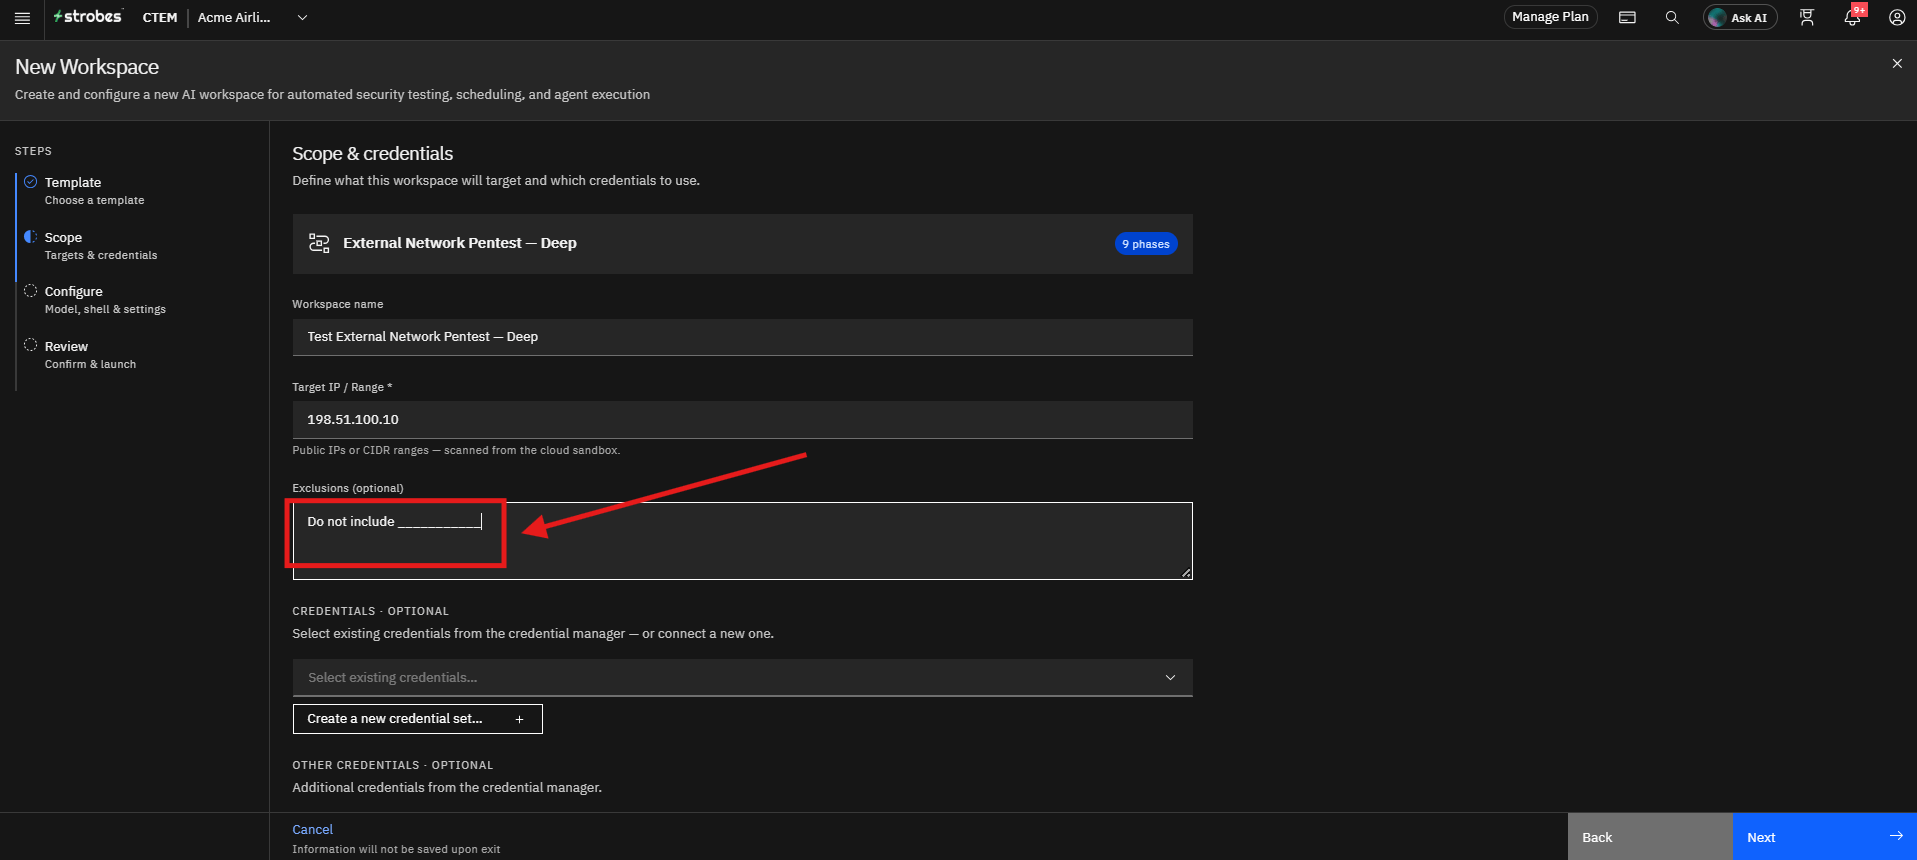
Step 3: Add Exclusions (Optional)
In the Exclusions field, enter any IPs or ports to leave out of scope. Use this to protect fragile or business-critical systems from testing.
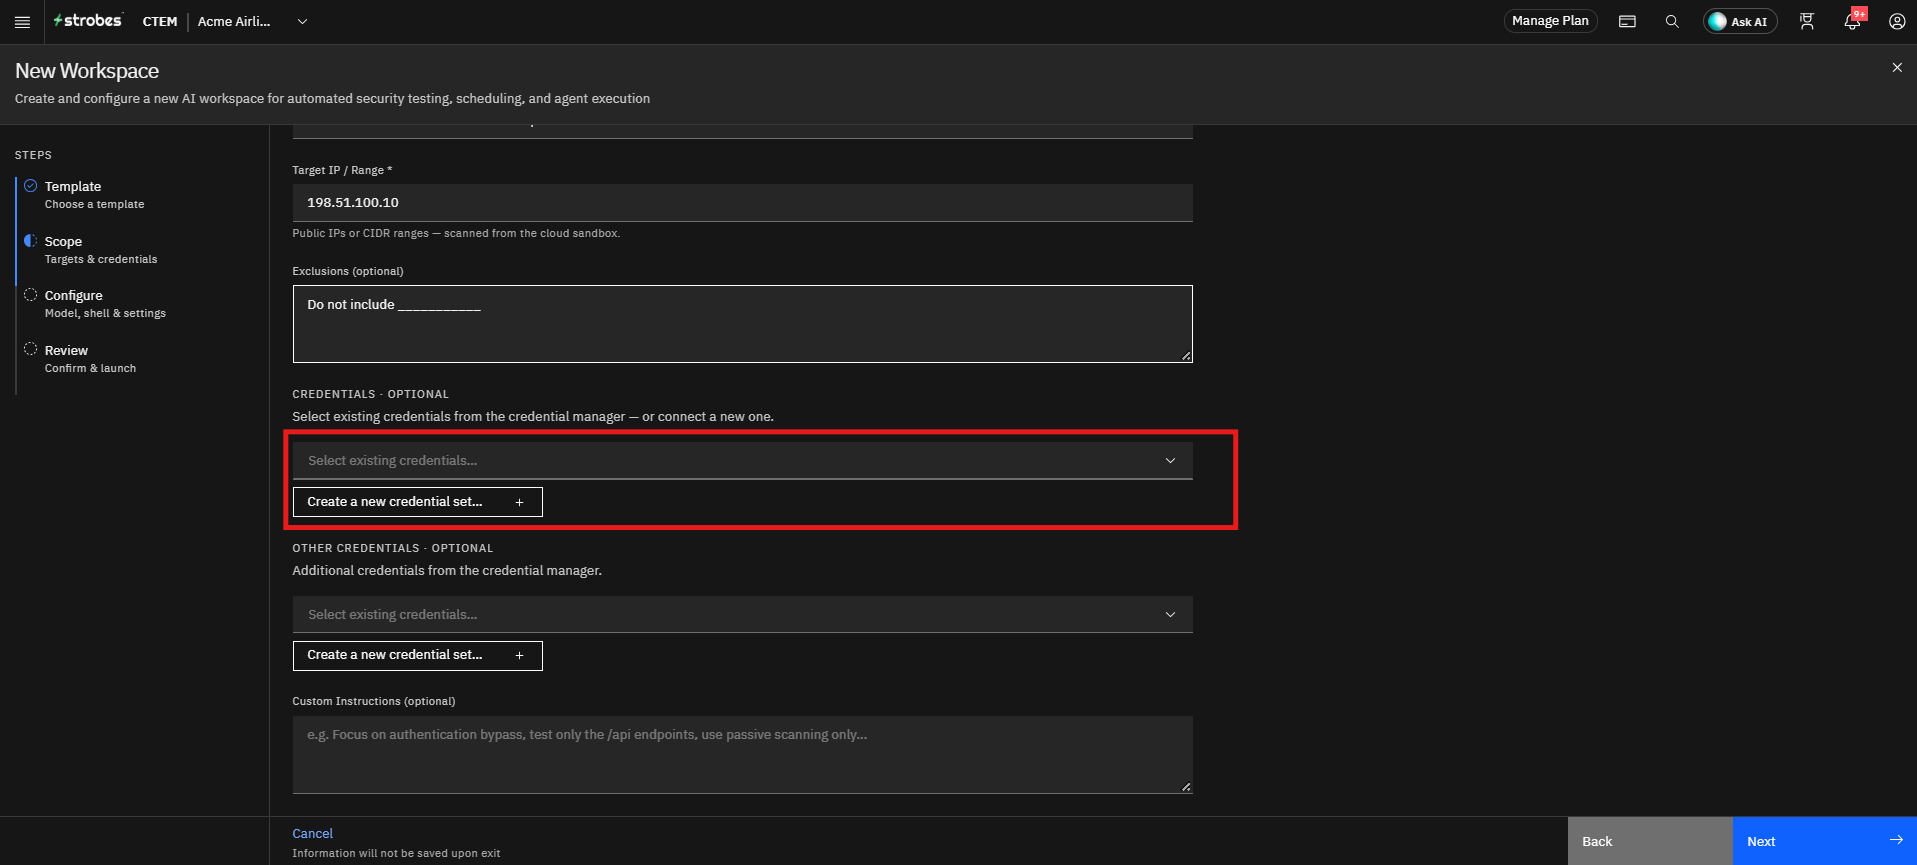
Step 4: Select Credentials (Optional)
Under Credentials, select existing credentials from the credential manager, or click Create a new credential set to add new ones.
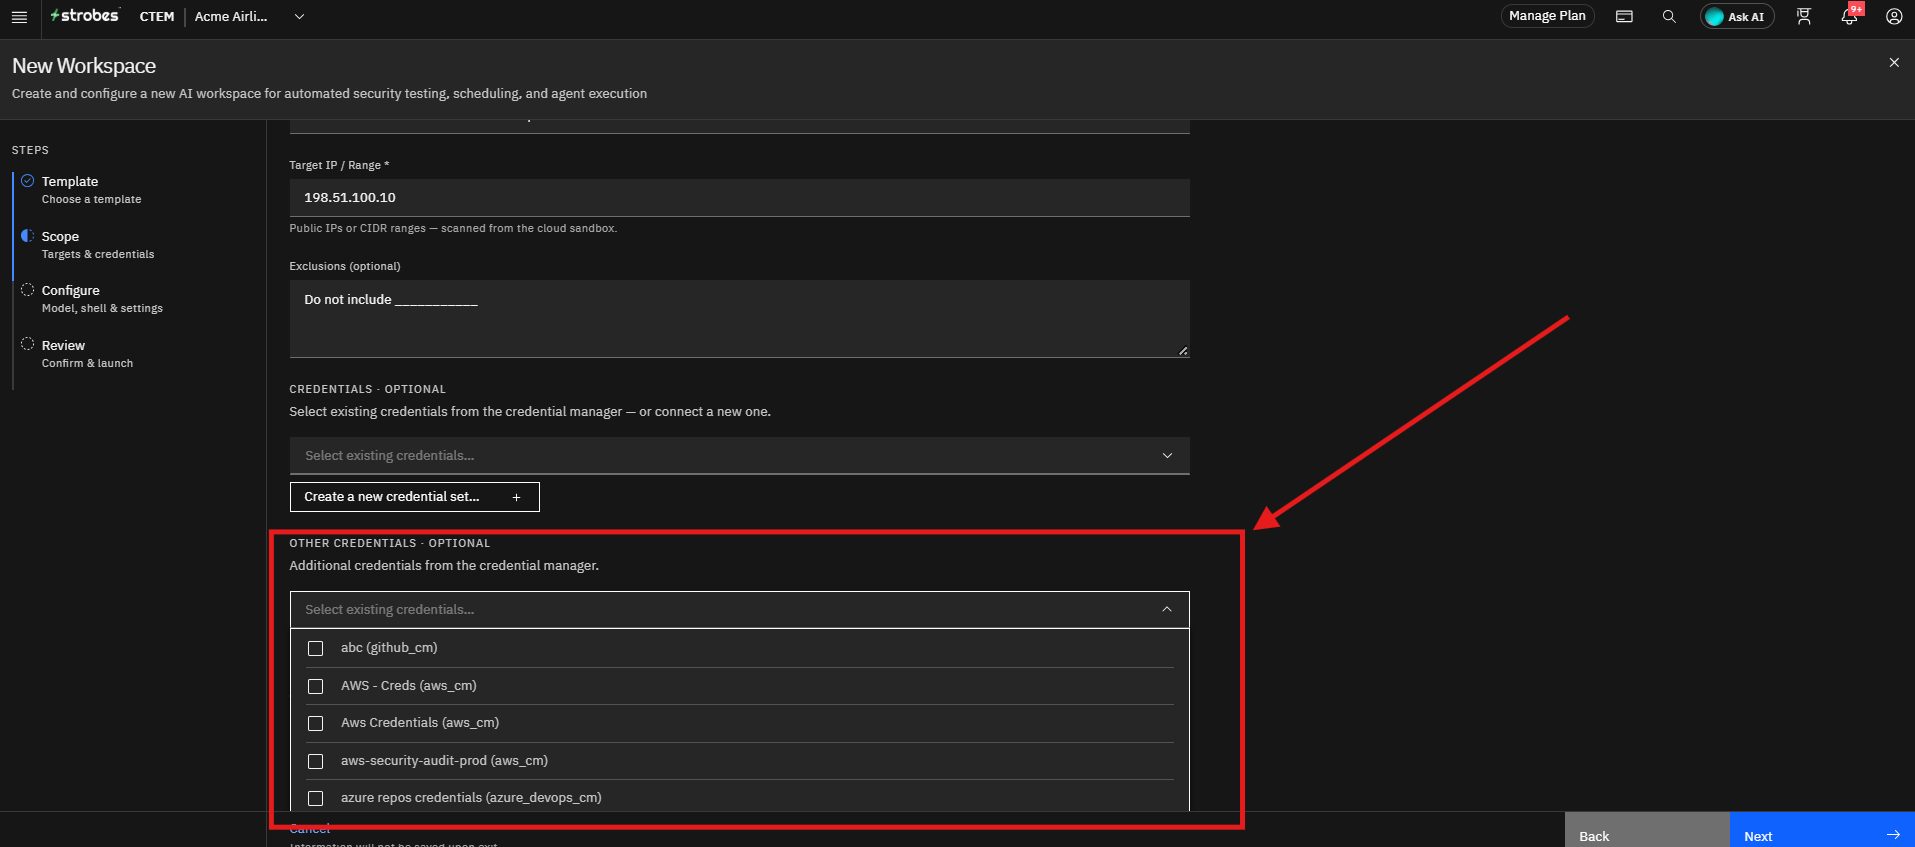
Step 5: Add Other Credentials (Optional)
Under Other Credentials, select additional credentials from the credential manager, or click Create a new credential set to add them.
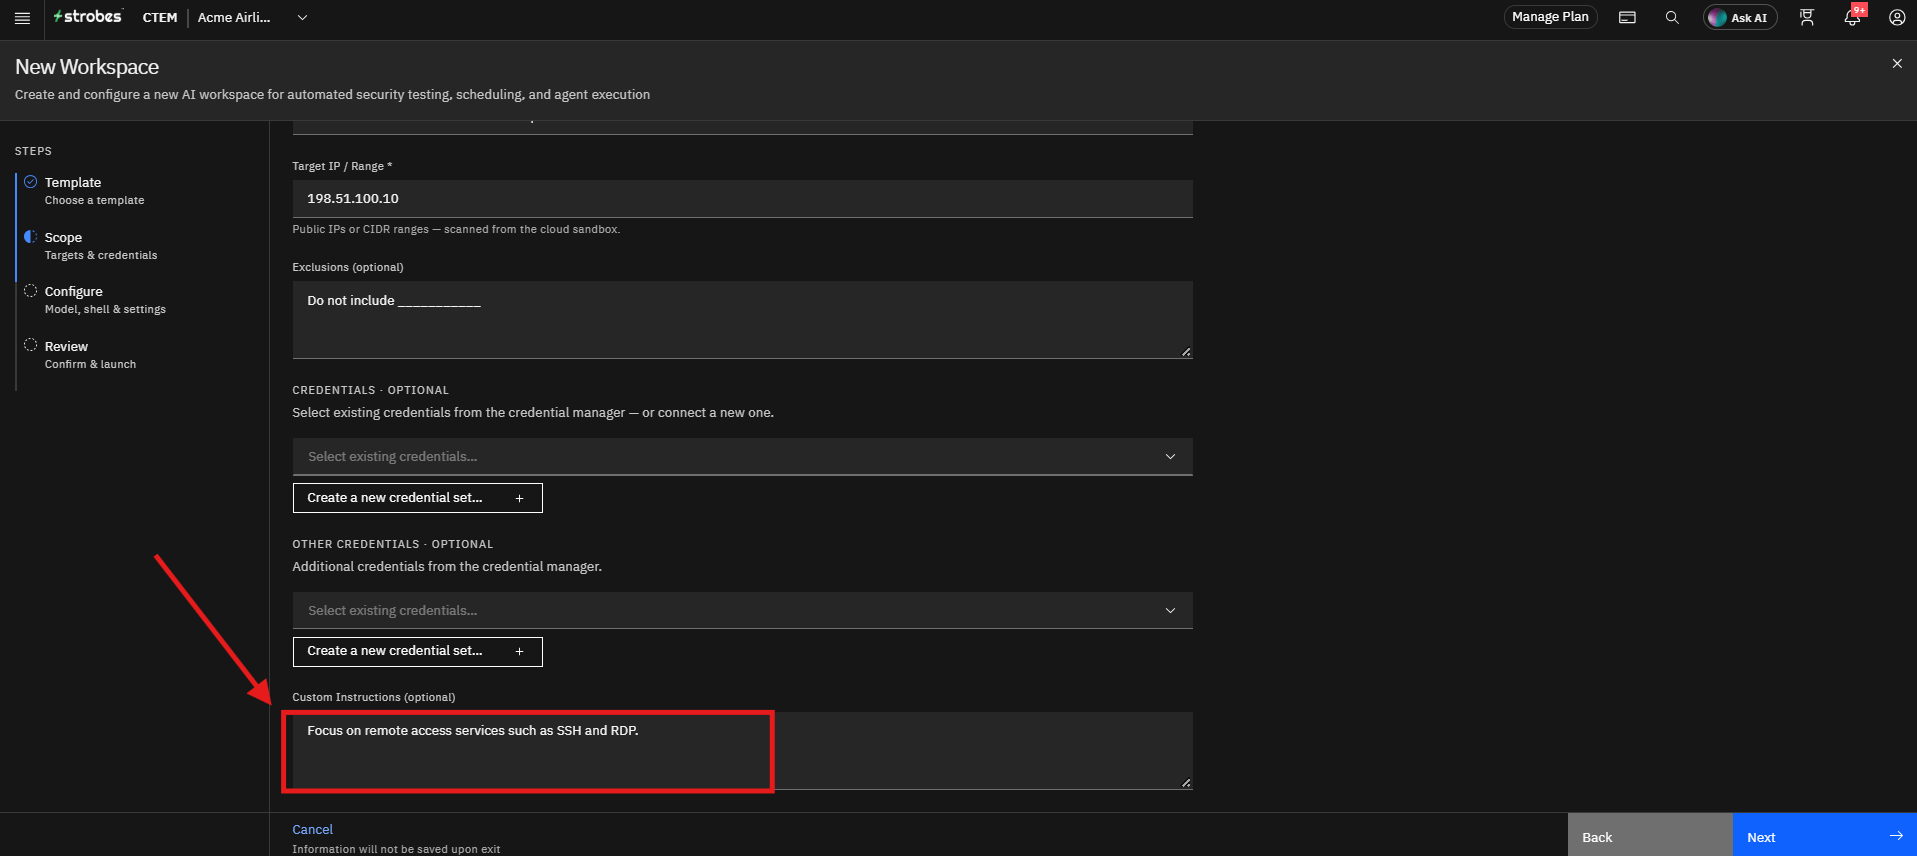
Step 6: Add Custom Instructions (Optional but highly recommended)
Use the Custom Instructions field to guide the assessment.
Example instructions:
- Focus on remote access services such as SSH and RDP.
- Prioritize services exposed to the internet.
- Skip denial-of-service style tests.
- Test only the web ports.
These instructions help tailor the AI analysis to specific objectives.
Proceeding to Configuration
After completing the scope details:
- Verify the target IPs or ranges and any exclusions.
- Review the credentials and instructions.
- Click Next.
The wizard proceeds to the Configure step, where the model, shell, and execution settings can be customized.
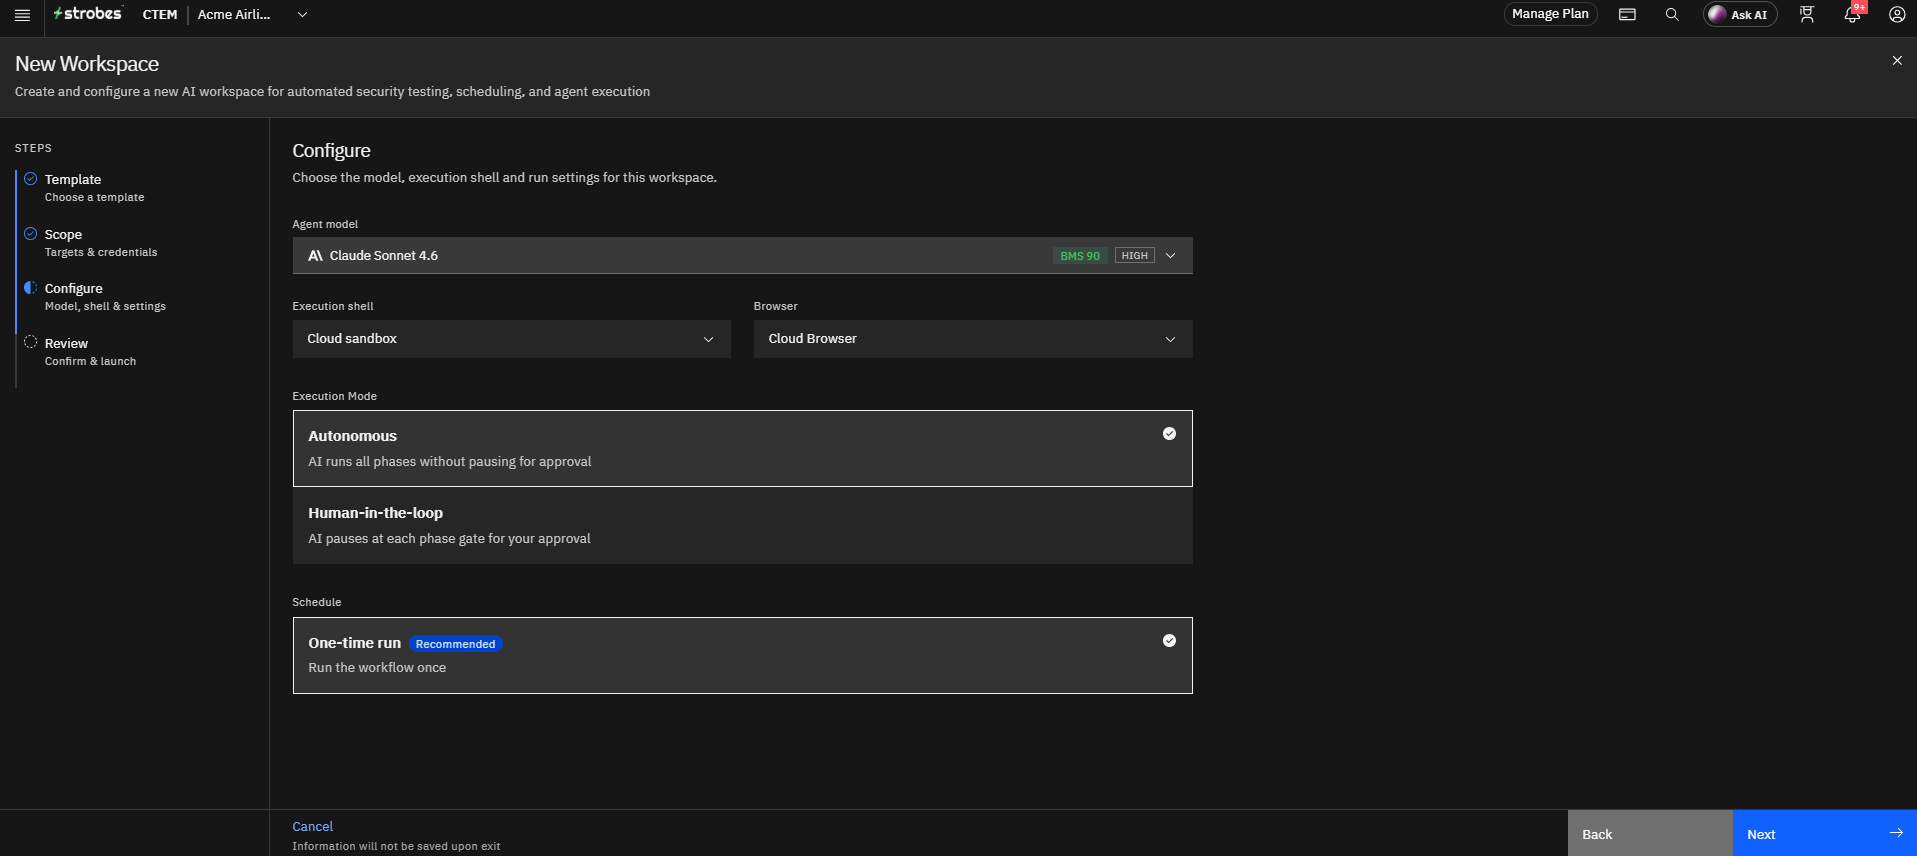
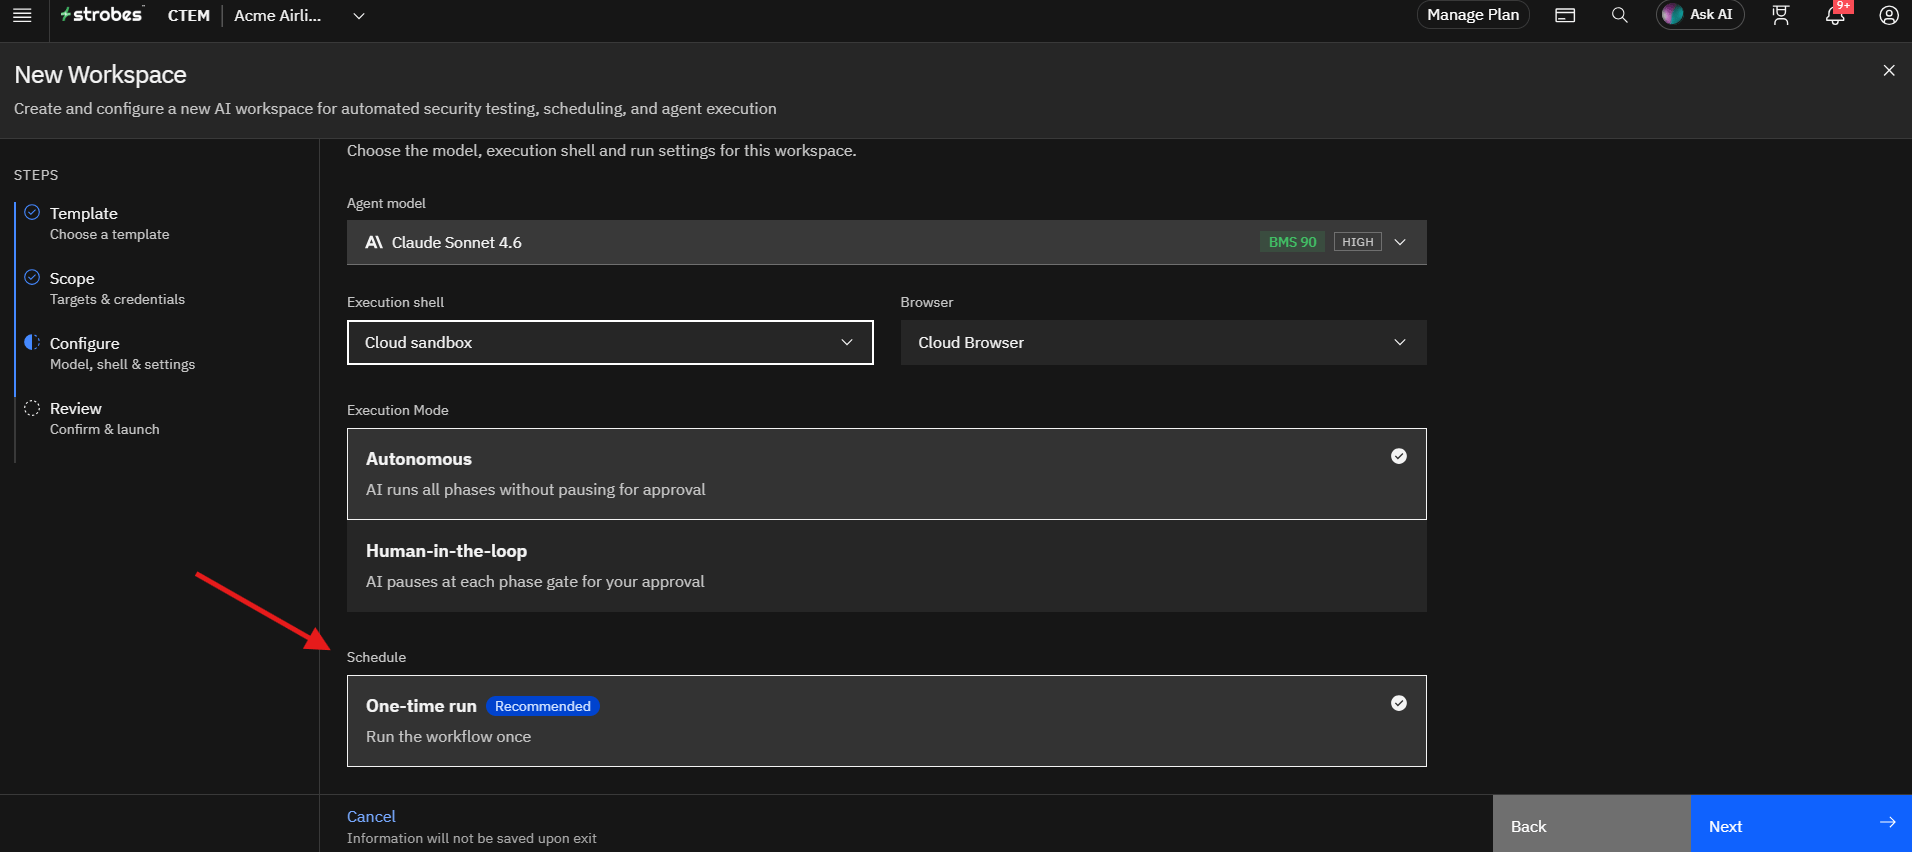
Step 7: Select an AI Model
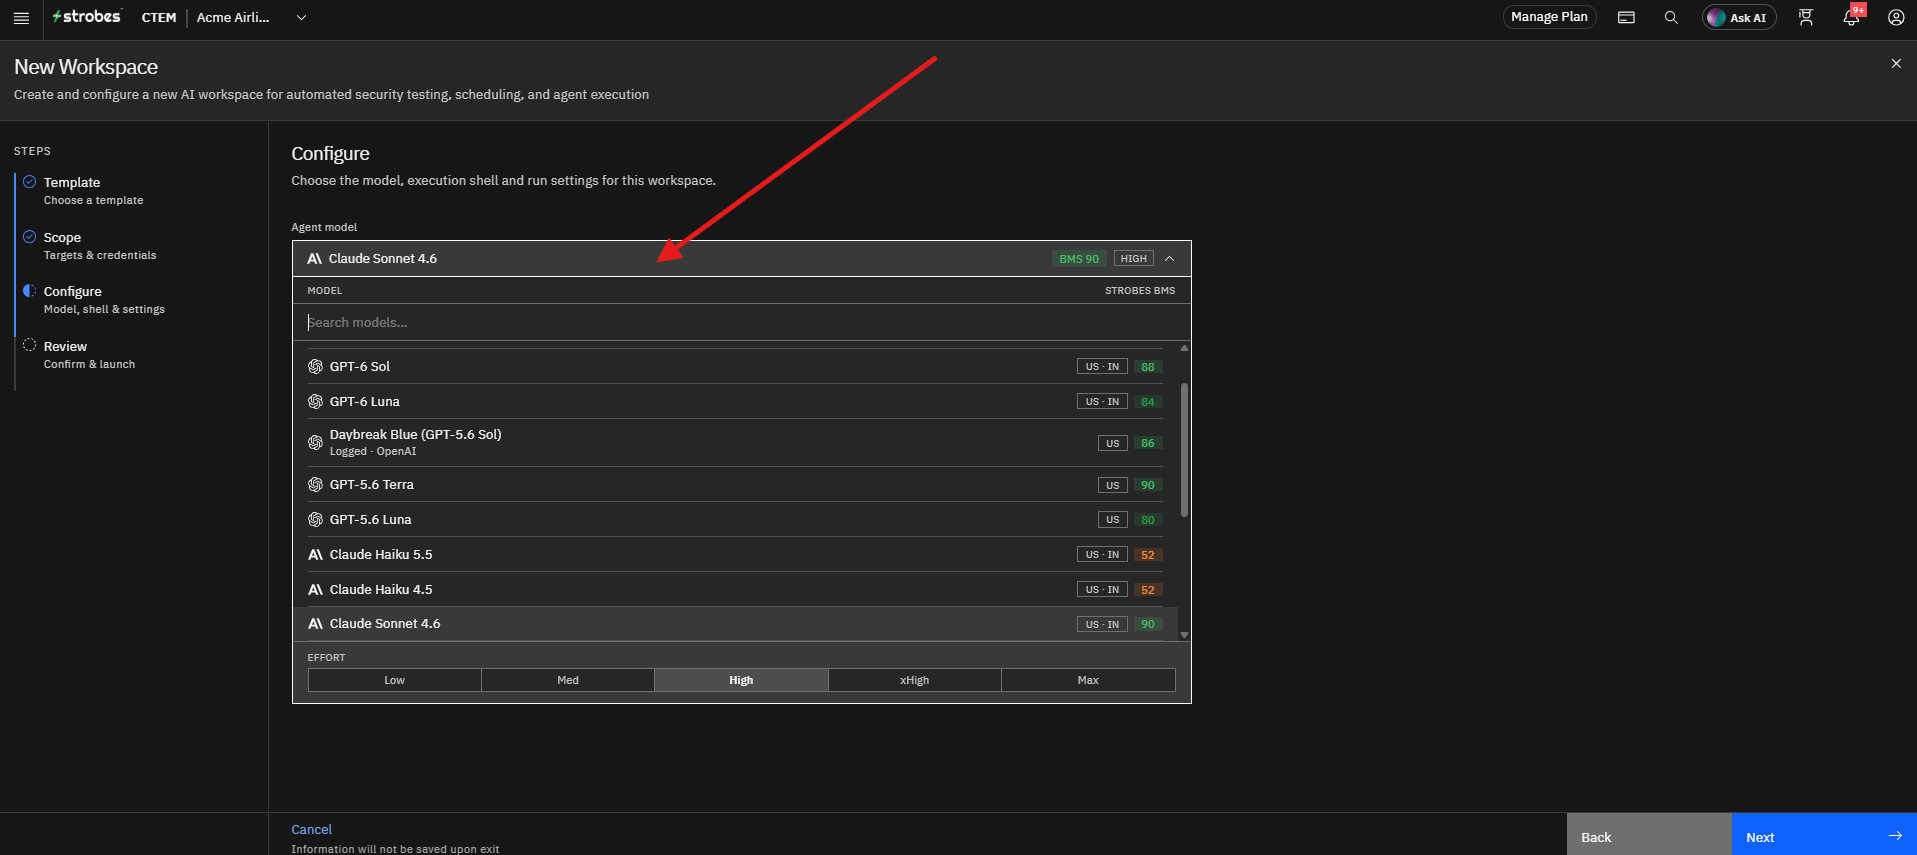
The Agent model determines the Large Language Model (LLM) used during the assessment.
To select a model:
- Open the Agent model dropdown.
- Review the available models and the effort level.
- Select the model that best fits your assessment requirements.
The selected model influences analysis depth, reasoning capabilities, response quality, and assessment speed.
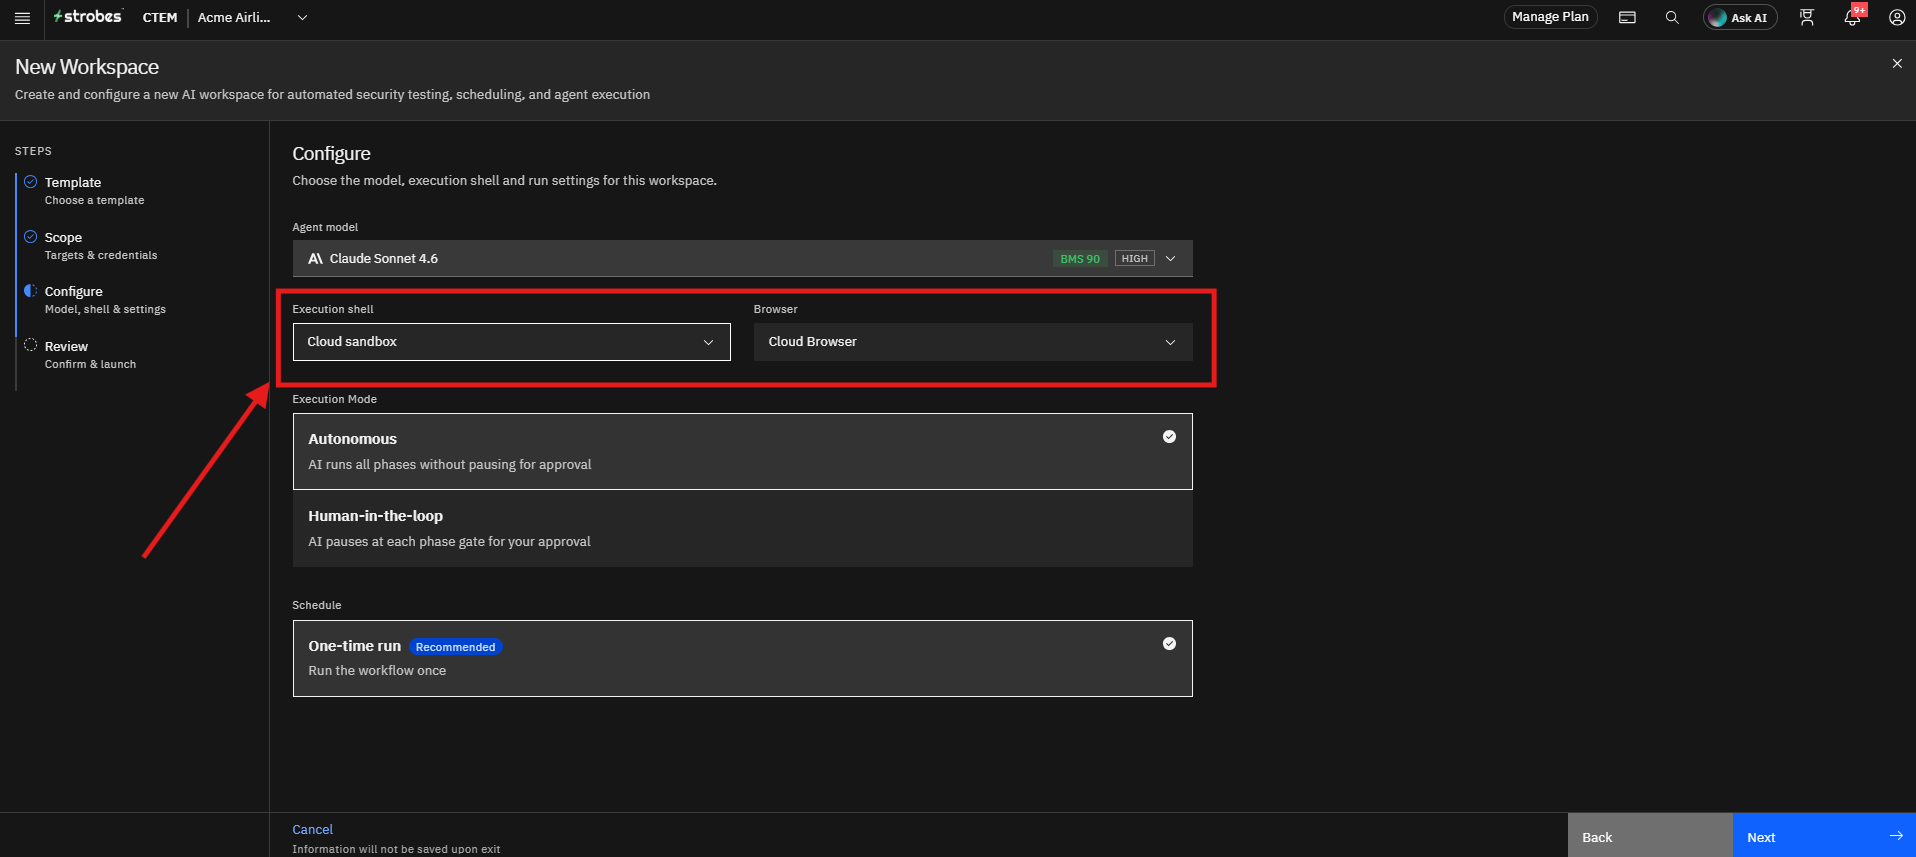
Step 8: Review the Execution Shell and Browser
The Execution shell is Cloud sandbox and the Browser is Cloud Browser by default. This is the recommended setup for external targets.
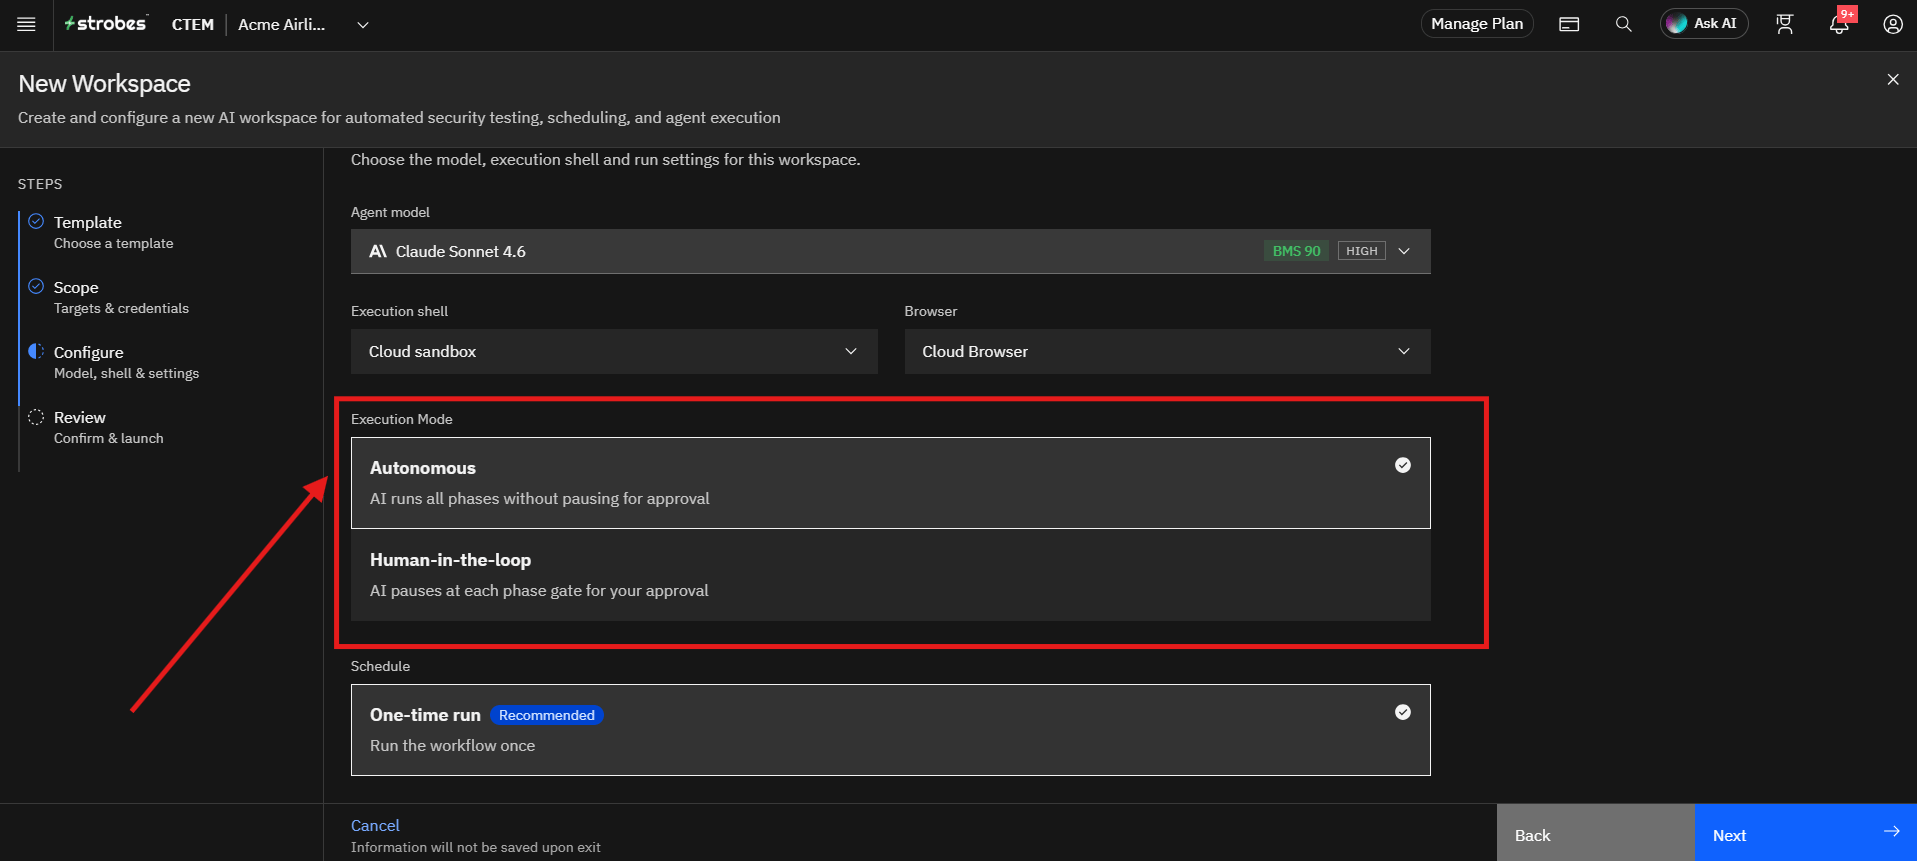
Step 9: Select the Execution Mode
Choose how the AI runs the assessment. Autonomous is selected by default.
- Autonomous: The AI runs all phases without pausing for approval.
- Human-in-the-loop: The AI pauses at each phase gate and waits for your approval before continuing.
Step 10: Review the Schedule
The workflow is set to One-time run by default, so it runs once.
Step 11: Continue to Review and Launch
Once all configuration settings have been verified:
- Click Next.
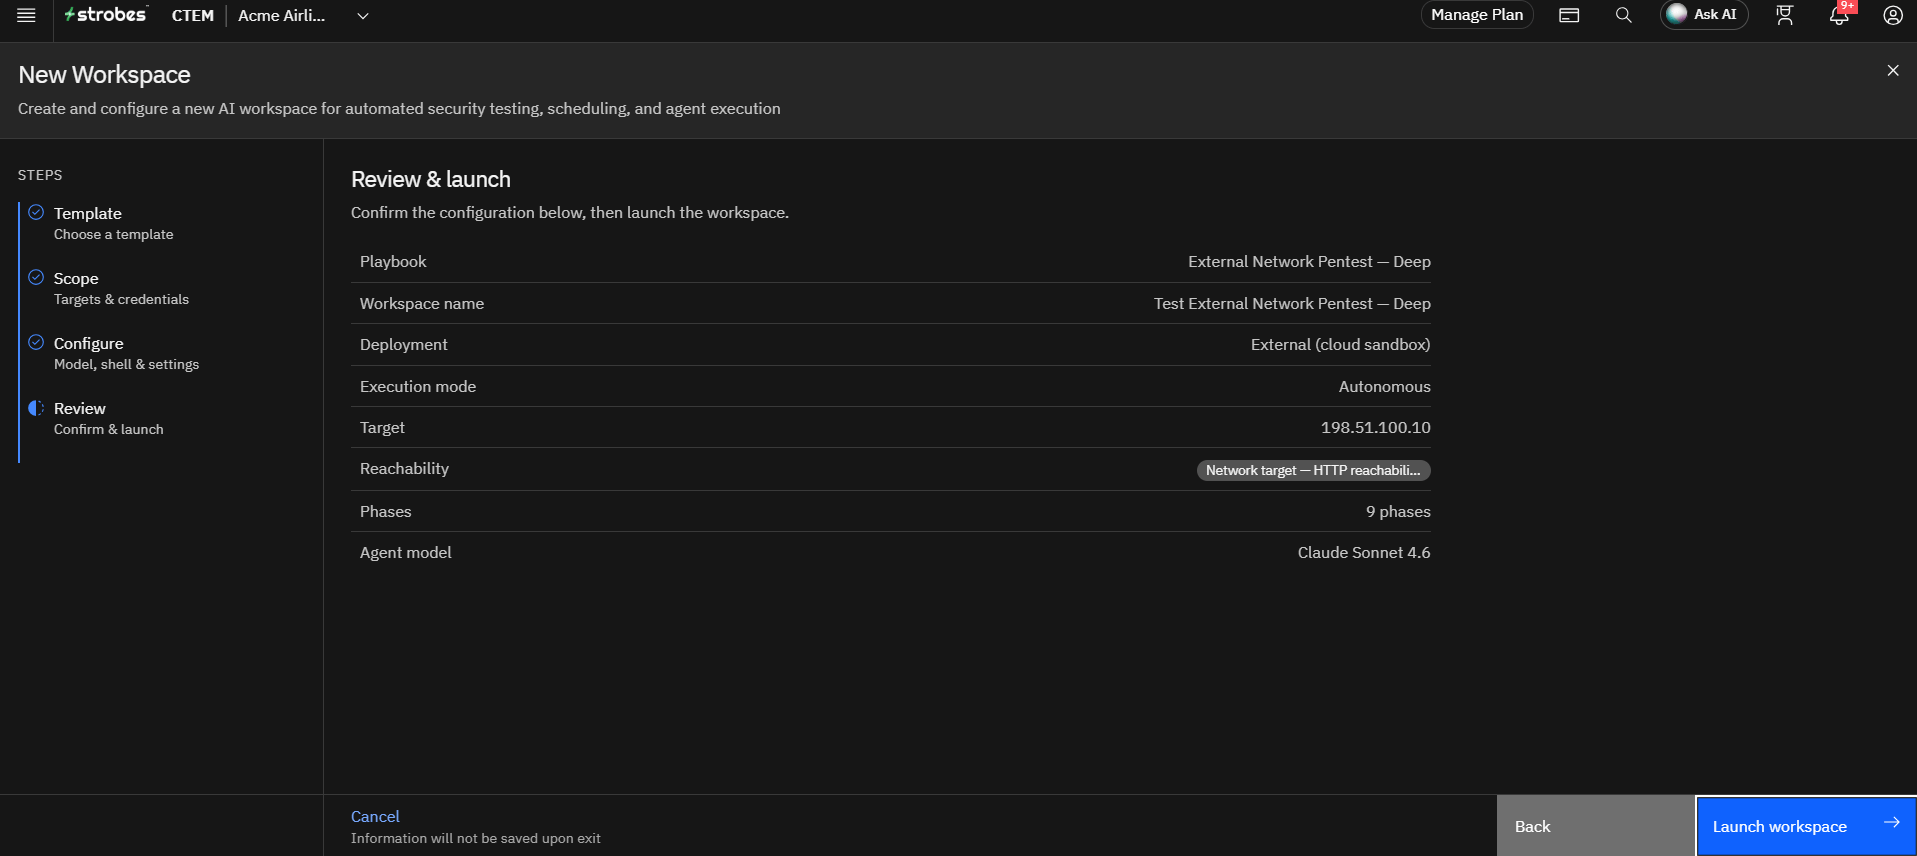
- The wizard opens the Review page.
Step 12: Review and Launch the Workspace
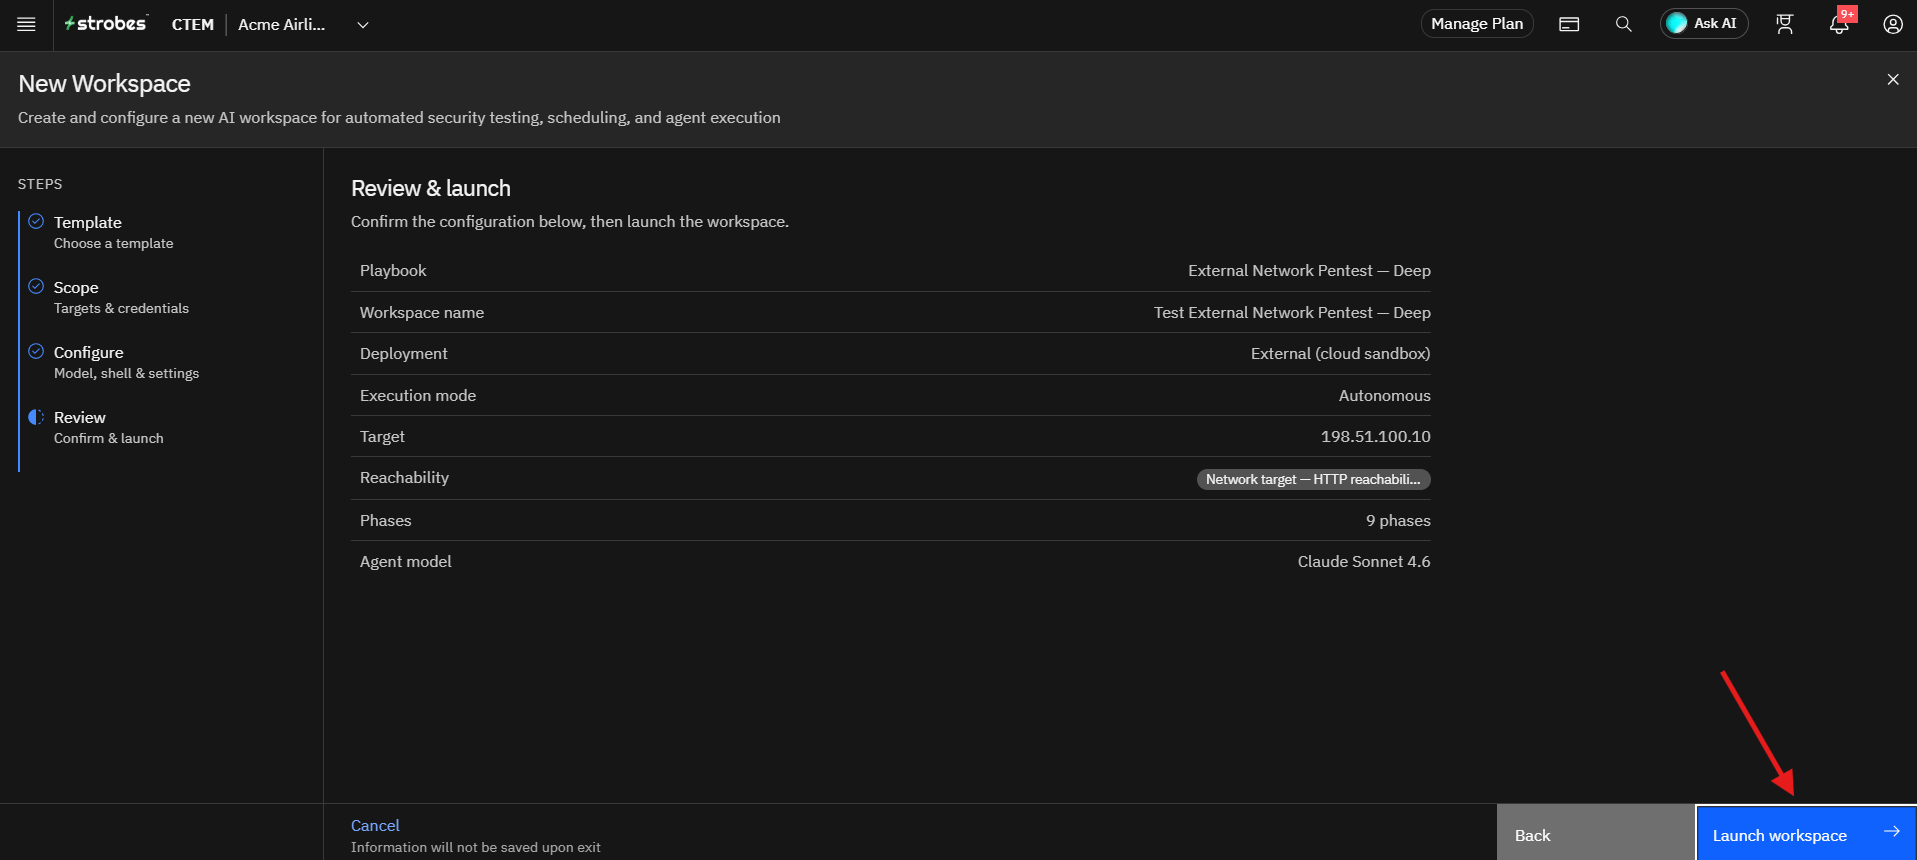
Review the configuration summary, including the playbook, workspace name, deployment, execution mode, target, phases, and agent model.
Strobes automatically checks whether the target is reachable. Once everything looks correct, click Launch workspace to start the assessment. When the run completes, findings appear in Strobes linked to your assets, and the report is available in the workspace.
Tips
- The Target IP / Range is required. The Next button stays unavailable on the Scope step until a valid entry is provided.
- Start with Standard if you are unsure. Use Fast for quick checks, and Deep for your most critical environments.
- Use Exclusions to keep fragile or business-critical systems out of the test.
- Use Human-in-the-loop for sensitive environments, so you can approve each phase before it continues.
- Only public IPs and CIDR ranges can be scanned from the cloud sandbox. For private networks, use the Internal Network Pentest template.
- Custom instructions are optional but can help focus the assessment, for example by limiting testing to specific services or ports.
- The assessment duration varies based on the template and the size of the target range.
- Only test networks and systems you are authorized to test.
More in Workspace configuration
Was this page helpful?