Compliance and Framework Reporting in Strobes AI Penetration Testing
Overview
Strobes AI Penetration Testing provides compliance and security framework reporting capabilities to help organizations analyze penetration testing findings against industry standards and regulatory requirements.
The AI-powered reporting engine generates structured reports using the actual findings identified during a security engagement. Reports can be generated using supported compliance frameworks or through custom, plain-language requests for specific standards.
Supported Compliance Frameworks
Strobes currently supports the following compliance frameworks directly within the AI Pentest workspace:
Framework | Description |
|---|---|
PCI DSS | Payment Card Industry Data Security Standard |
SOC 2 | Service Organization Control 2 |
ISO 27001 | Information Security Management System standard |
HIPAA | Health Insurance Portability and Accountability Act |
NIST CSF | NIST Cybersecurity Framework |
CIS Controls | Center for Internet Security Controls |
These frameworks are available through the built-in compliance reporting functionality in the AI Pentest workspace.
Generate a Compliance Report
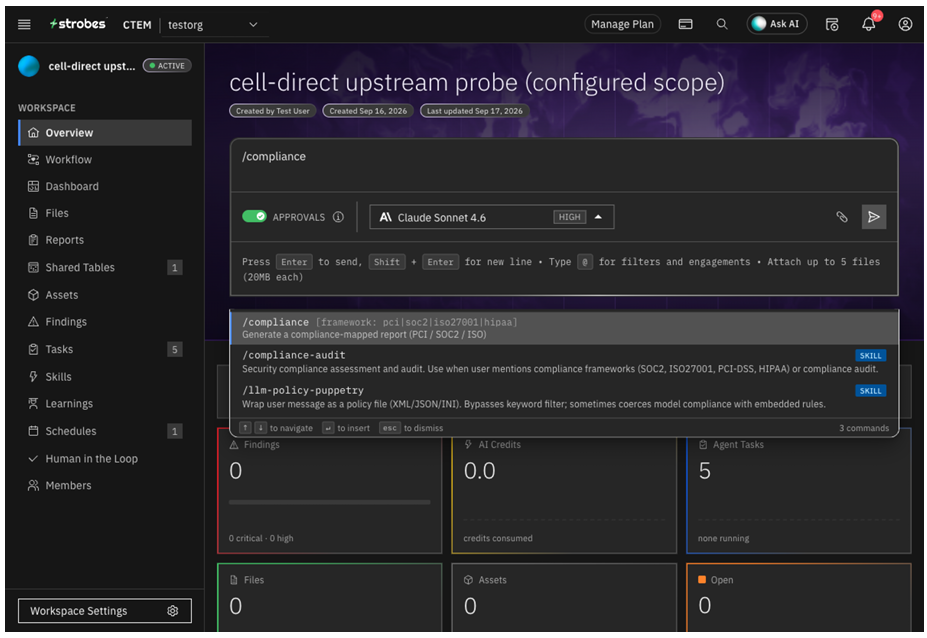
You can generate a compliance report directly from the AI Pentest workspace chat.
Step 1: Open the AI Pentest Workspace
Navigate to the AI Pentest workspace containing the relevant security engagement.
Step 2: Open the Workspace Chat
Open the AI-powered chat interface available within the engagement.
Step 3: Use the Compliance Command
Enter the following command in the chat:
/compliance
Step 4: Select a Framework
Choose the required compliance framework from the available options.
Step 5: Generate the Report
Strobes AI analyzes the findings from the engagement and generates a structured report mapped to the selected framework.
Contents of a Compliance Report
A compliance report may include the following sections:
- Executive Summary
- Framework Control Mapping
- Findings Mapped to Relevant Controls
- Unmapped Findings Appendix
The report is generated based on the actual findings available in the engagement.
Custom Framework Reporting
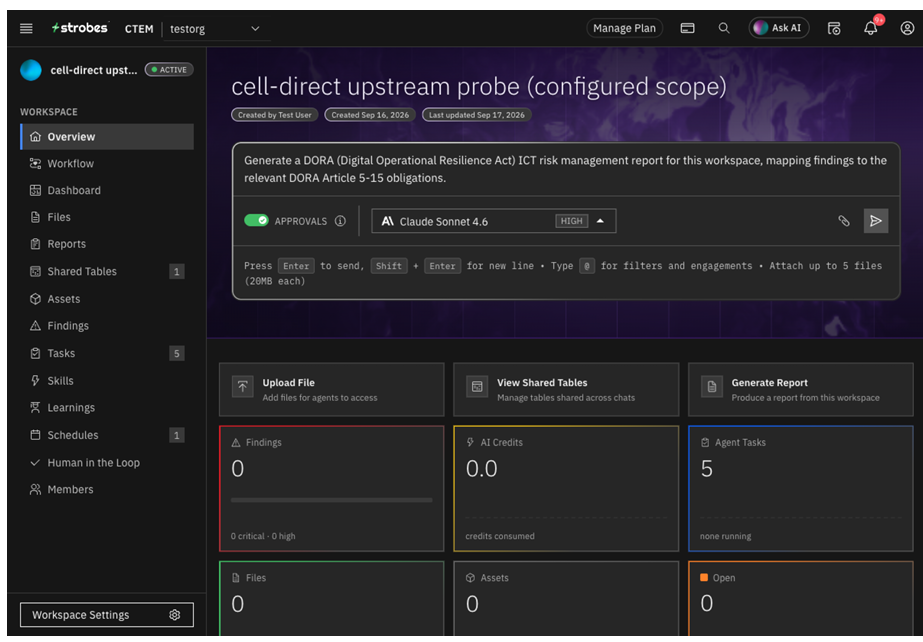
In addition to the supported compliance frameworks, Strobes AI allows users to request reports based on other security standards and regulatory frameworks using natural language.
For example, users can request reports structured against:
- DORA (Digital Operational Resilience Act)
- NIS2 Directive
- PTES (Penetration Testing Execution Standard)
- NIST SP 800-115
Example Request
Generate a report structured against DORA ICT risk requirements and map the relevant findings from this engagement.
The AI reporting engine uses the findings from the engagement to generate the requested report structure.
Finding Taxonomy and Compliance Mapping
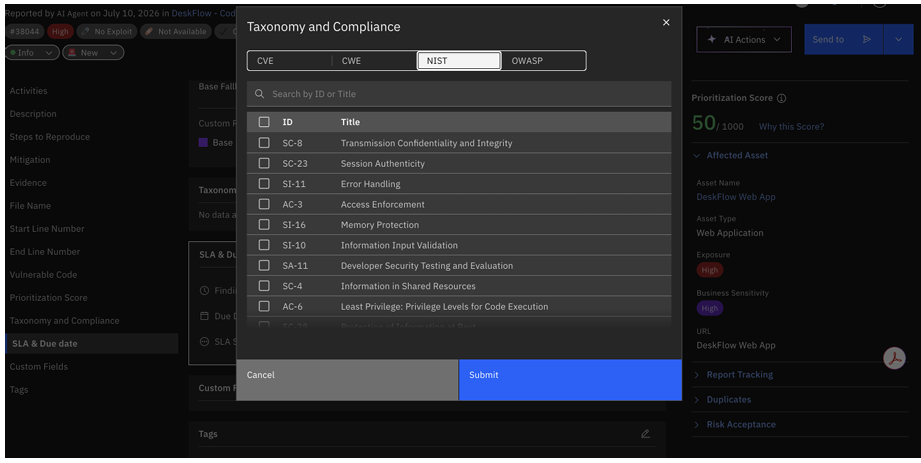
Each finding in Strobes includes a Taxonomy and Compliance section that allows security findings to be associated with industry-standard identifiers and compliance references.
Supported Taxonomies
Taxonomy / Standard | Availability |
|---|---|
CVE | Supported |
CWE | Supported |
OWASP | Supported |
NIST SP 800-53 | Supported |
These mappings are stored as structured data and can be searched and selected within the finding details.
CVE, CWE, and OWASP references can be automatically associated with findings created or updated by AI agents. NIST SP 800-53 mappings can also be added through the Taxonomy and Compliance section.
OWASP Framework Mapping in Penetration Testing Reports
Strobes AI supports security framework mapping for different types of penetration testing engagements.
The following standards are supported across specific testing methodologies:
Penetration Testing Type | Associated Security Standard |
|---|---|
Mobile Application Pentest | OWASP MASVS / MASTG |
Web Application Pentest | OWASP WSTG |
API Security Testing | OWASP API Top 10 |
LLM / Agentic Chatbot Pentest | OWASP LLM Top 10 |
These mappings help organizations organize penetration testing findings according to recognized security standards.
Report Formats
Strobes AI supports professionally formatted report outputs, including:
- PowerPoint (PPTX)
Reports are generated using predefined templates to maintain consistent formatting and presentation.
Important Information
- Compliance reports are generated based on findings available within the security engagement.
- Framework mappings depend on the findings and taxonomy information associated with the engagement.
- Custom framework reports can be requested using plain-language instructions through the AI Pentest workspace chat.
- Report availability may vary depending on the configured AI Pentest capabilities and framework support.
Summary
Strobes AI Penetration Testing helps organizations generate compliance and framework-based security reports using their existing penetration testing findings.
Key capabilities include:
- Built-in compliance reporting for PCI DSS, SOC 2, ISO 27001, HIPAA, NIST CSF, and CIS Controls.
- Custom framework reporting through natural-language requests.
- Structured taxonomy mapping for CVE, CWE, OWASP, and NIST SP 800-53.
- OWASP framework mapping for different penetration testing methodologies.
- Professionally formatted PDF and PowerPoint reports.
These capabilities provide a centralized and flexible approach to compliance-focused security reporting.