Connecting Tenable Cloud Security to Strobes
Overview
The Tenable Cloud Security connector enables you to bring cloud security findings from Tenable CS directly into Strobes. Once configured, the connector helps centralize cloud security data, providing visibility into risks and vulnerabilities across your cloud environment for effective monitoring and remediation.
Supported Version
Cloud-based (SaaS)
Strobes connects directly to the customer's Tenable Cloud Security environment. The integration works with the version currently provided by Tenable Cloud Security, so no separate version tracking or upgrades are required within Strobes.
Tenable CS Connector Details
Field | Details |
|---|---|
Supported products | |
Category | Cloud Security Posture Management (CSPM) |
Ingested asset type(s) | Cloud Resources (e.g., VMs, storage buckets — same shape as MS Defender for Cloud's cloud assets) |
Integration type | UNI directional (data is transferred from the Connector to the Strobes Platform in one direction) |
Supported version and type | Cloud-based (SaaS) — latest |
Required Credentials
To configure the Tenable Cloud Security connector in Strobes, the customer must provide the following details from their Tenable Cloud Security account:
- URL — The URL of the customer's Tenable Cloud Security instance.
- Access Key — A single API key used to authenticate the connection between Tenable Cloud Security and Strobes. Unlike some connectors, Tenable CS requires only one access key and does not require a separate username and password.
Setting It Up in Strobes
To configure the Tenable Cloud Security connector in Strobes, enter the following details:
- URL — Enter the URL of your Tenable Cloud Security instance.
- Access Key — Enter the API key used to authenticate the connection.
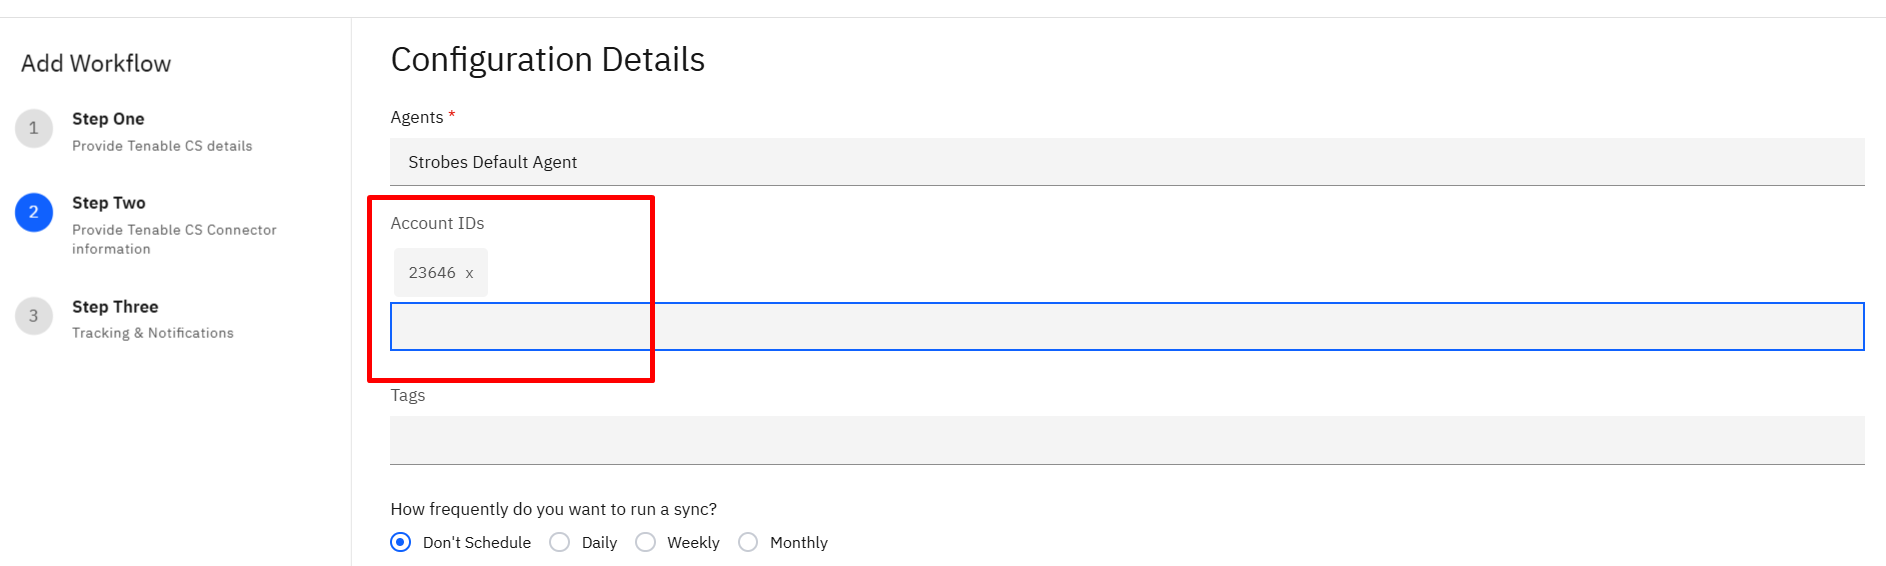
Account IDs (Optional)
The Account IDs field allows you to limit the sync to specific cloud accounts connected to your Tenable Cloud Security tenant.
What are Account IDs and Why Are They Used?
A Tenable Cloud Security tenant can be connected to multiple cloud accounts across platforms such as AWS, Azure, and GCP. In some cases, customers may want to sync findings only from selected cloud accounts instead of importing data from their entire environment.
For example, if a customer has 50 cloud accounts connected to Tenable Cloud Security but only 10 are relevant for production security tracking in Strobes, they can enter the specific account IDs they want to sync.
This helps customers control the scope of data imported into Strobes.
- If Account IDs are specified: Strobes syncs data only from the selected cloud accounts.
- If Account IDs are left blank: Strobes syncs data from all cloud accounts connected to the Tenable Cloud Security tenant.
What Data Comes into Strobes
Assets
Assets are imported into Strobes as cloud resources, such as virtual machines, storage buckets, and other resources available in the customer's Tenable Cloud Security environment.
If the customer also uses the Microsoft Defender for Cloud connector, the same cloud resource may be imported through both connectors. Strobes automatically identifies and merges duplicate assets to avoid creating multiple records for the same resource.
Findings
Findings imported from Tenable Cloud Security appear in Strobes as Alerts rather than standard Findings.
This is specific to how data from this connector is categorized within Strobes. If a customer asks why their Tenable CS findings are not visible under the Findings section, they should check the Alerts section instead.
How Status Is Kept in Sync
The status of alerts in Strobes is synchronized with the corresponding status in Tenable Cloud Security.
- When Tenable marks a security issue as resolved, Strobes automatically updates the matching alert to Resolved.
- If Tenable continues to report the issue as active, the alert remains New in Strobes.
This ensures that alert statuses in Strobes reflect the latest information from Tenable Cloud Security.
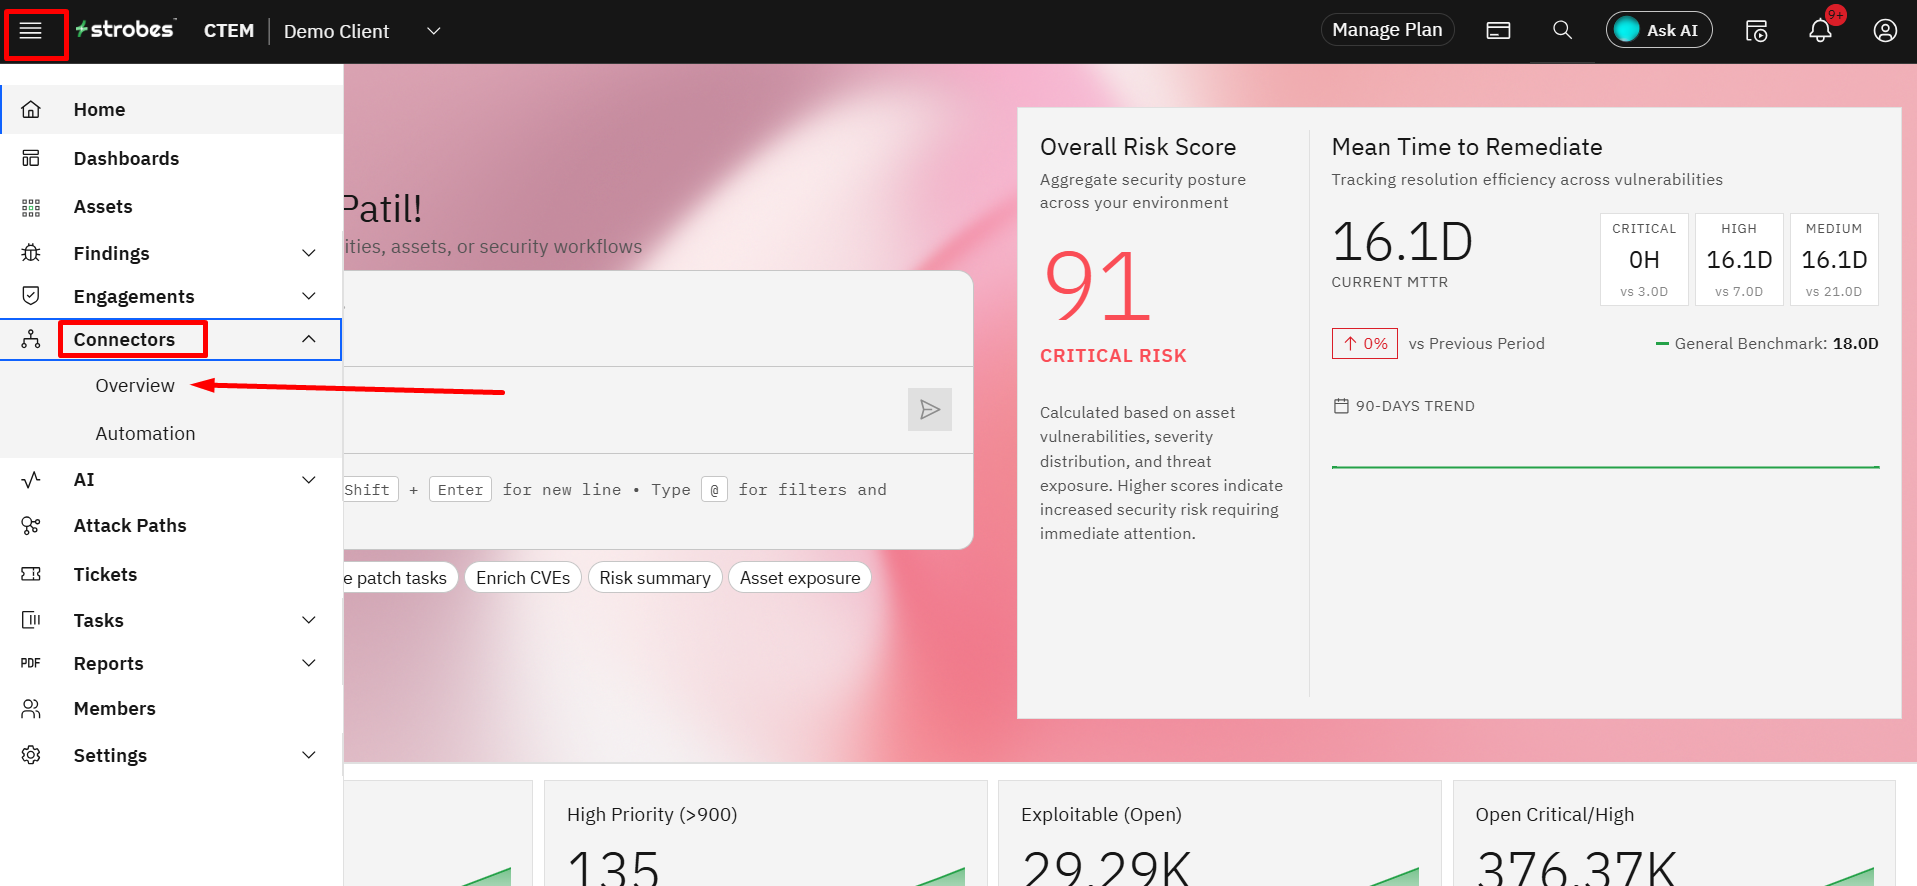
Step 1: Navigate to the Connectors
In the left navigation pane, expand Connectors and click Overview. The Connectors Overview page opens, displaying all installed and available connectors organized by category.
Step 2: Search for the Connector
In the Search bar, type Tenable CS. The Tenable CS connector is displayed under Available Connectors.
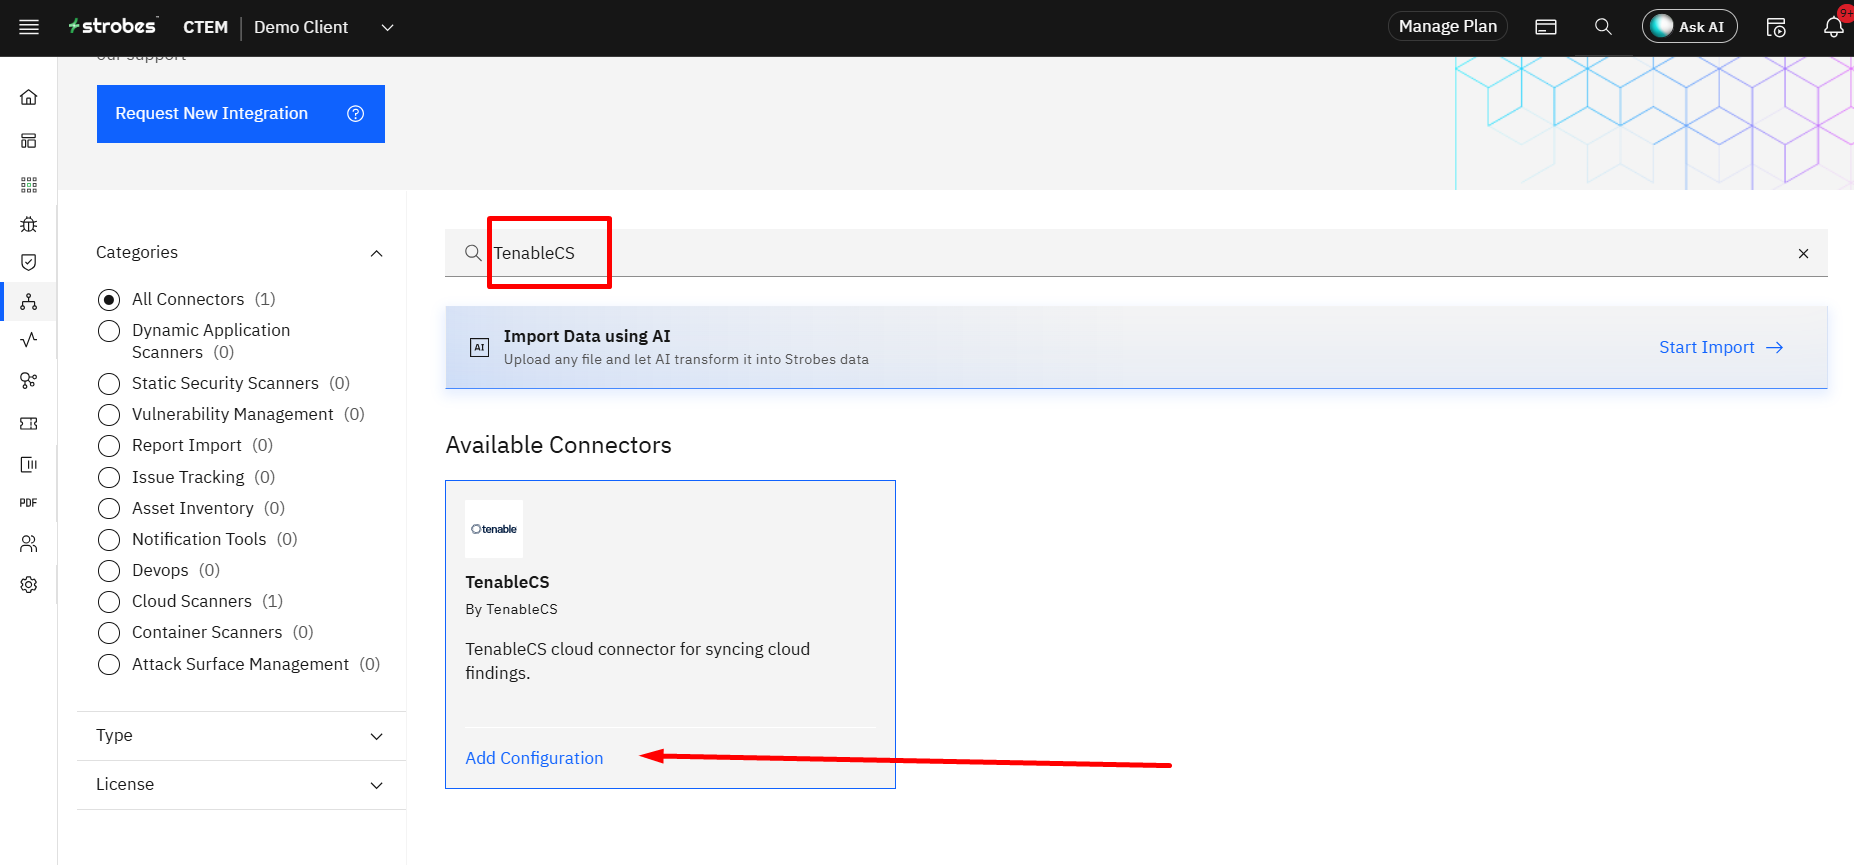
Step 3: Open the Connector
Click Add Configuration on the Tenable CS card. The Add Workflow panel opens with three steps listed in the left sidebar.
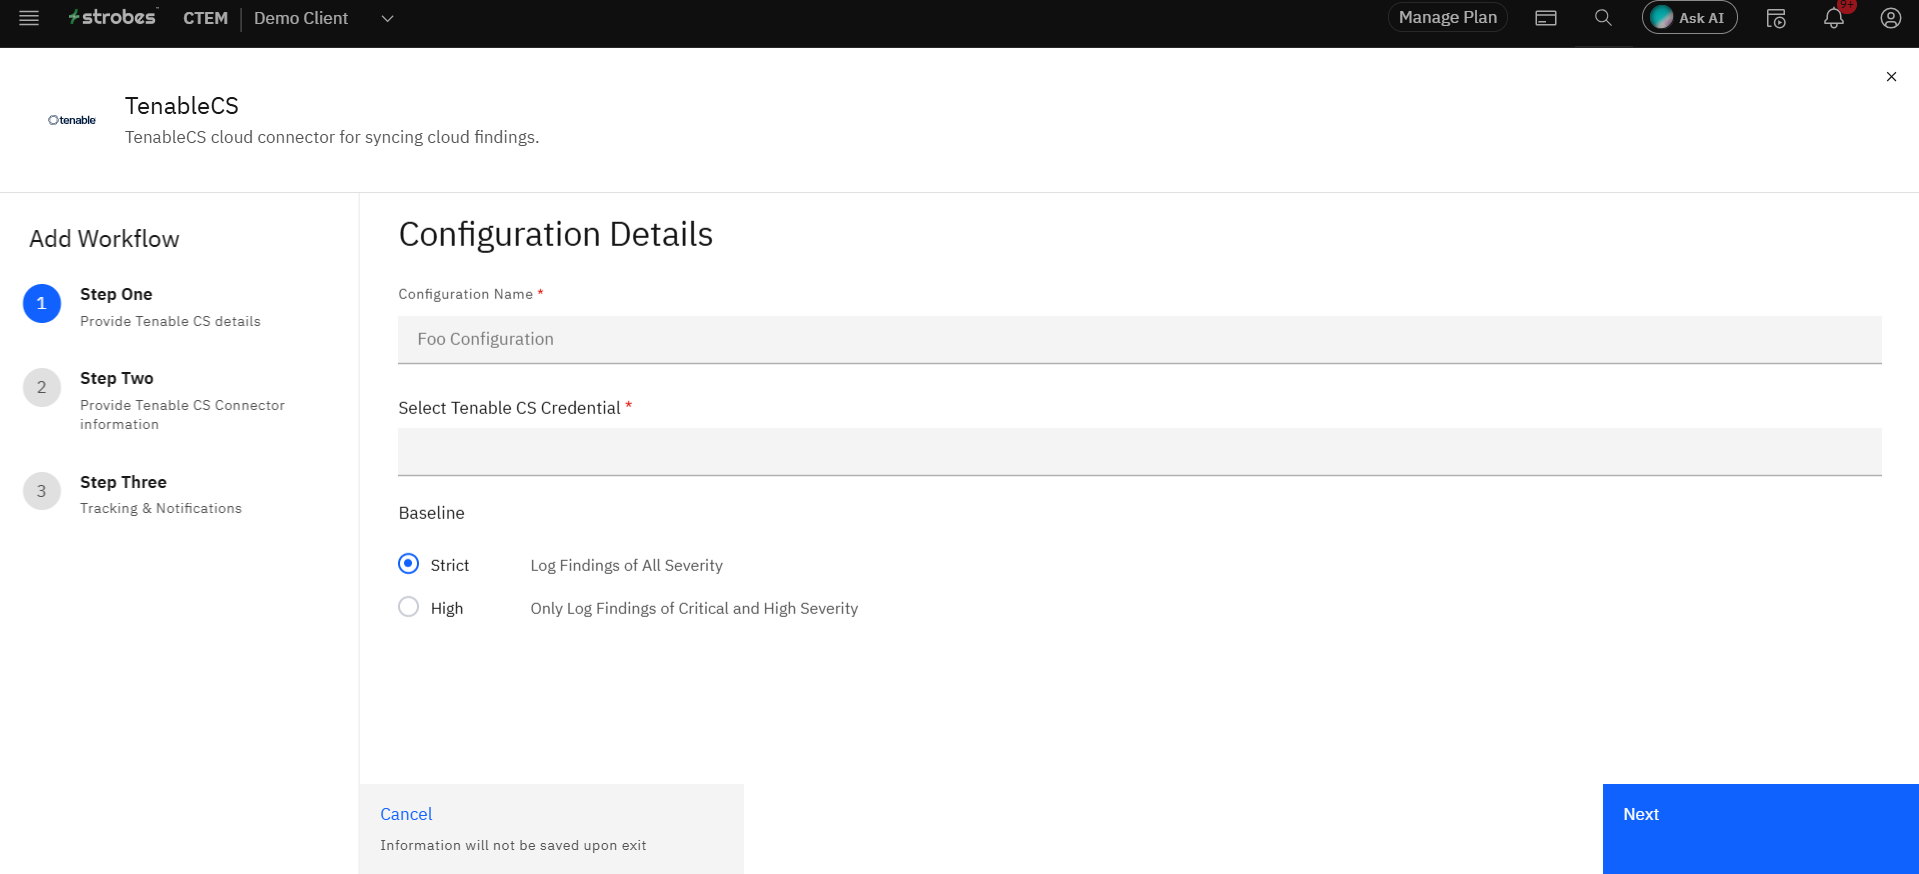
Step 4: Enter a Configuration Name
In the Configuration Name field, enter a unique name for the configuration. A green "Config name is available!" message confirms that the name is not already taken.
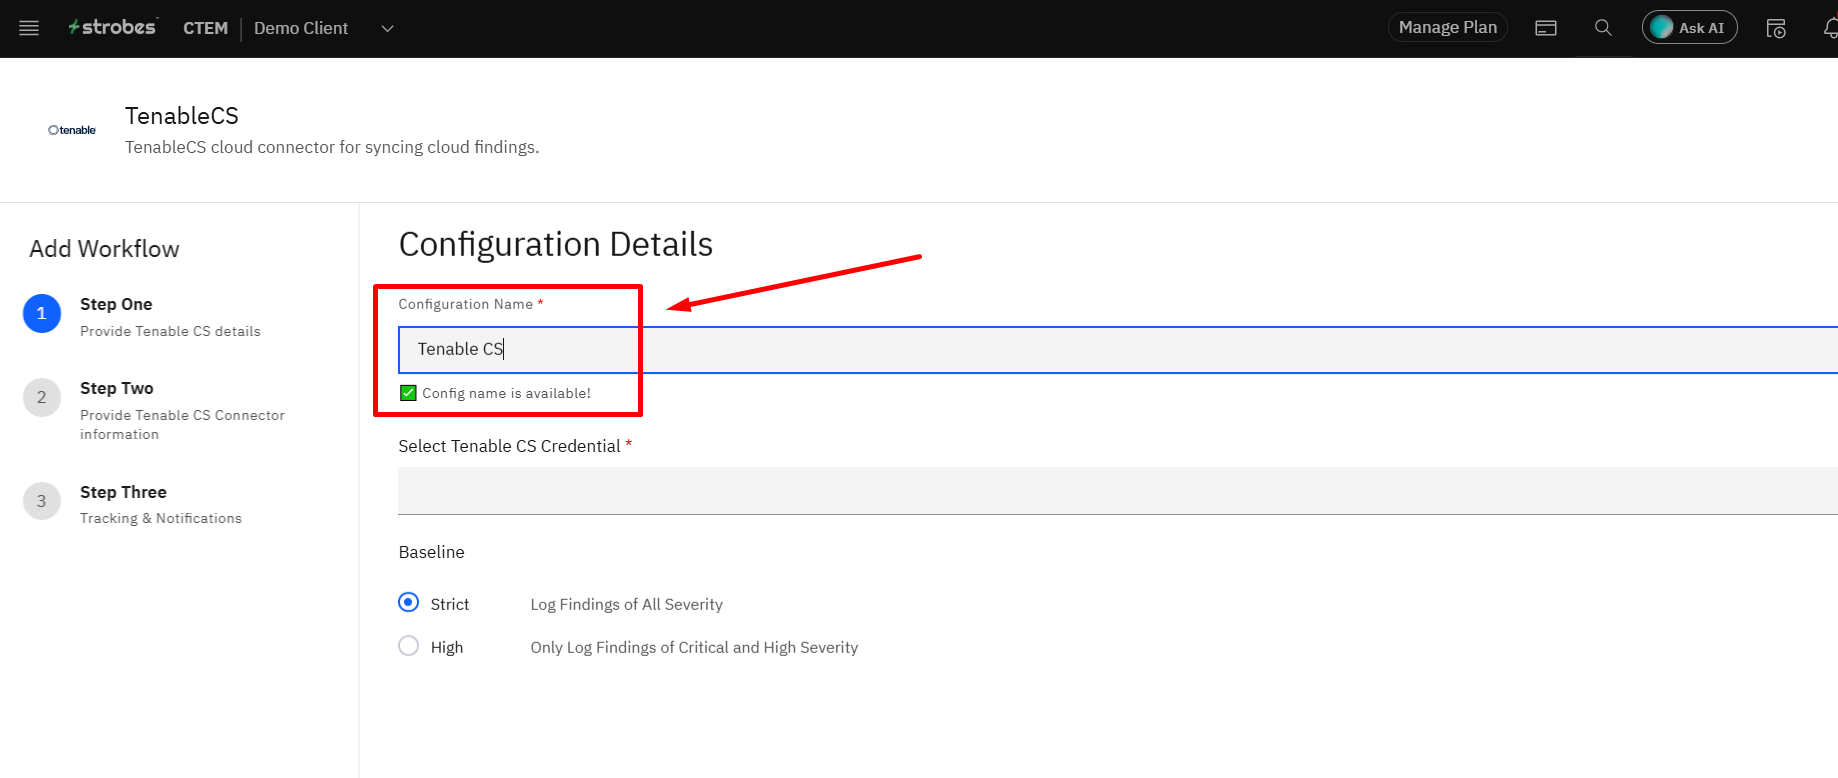
Step 5: Select Tenable CS Credentials
Click the Select Tenable Credential dropdown. If you have an existing saved credential, select it from the list. If not, click Create Credential to add a new credential.
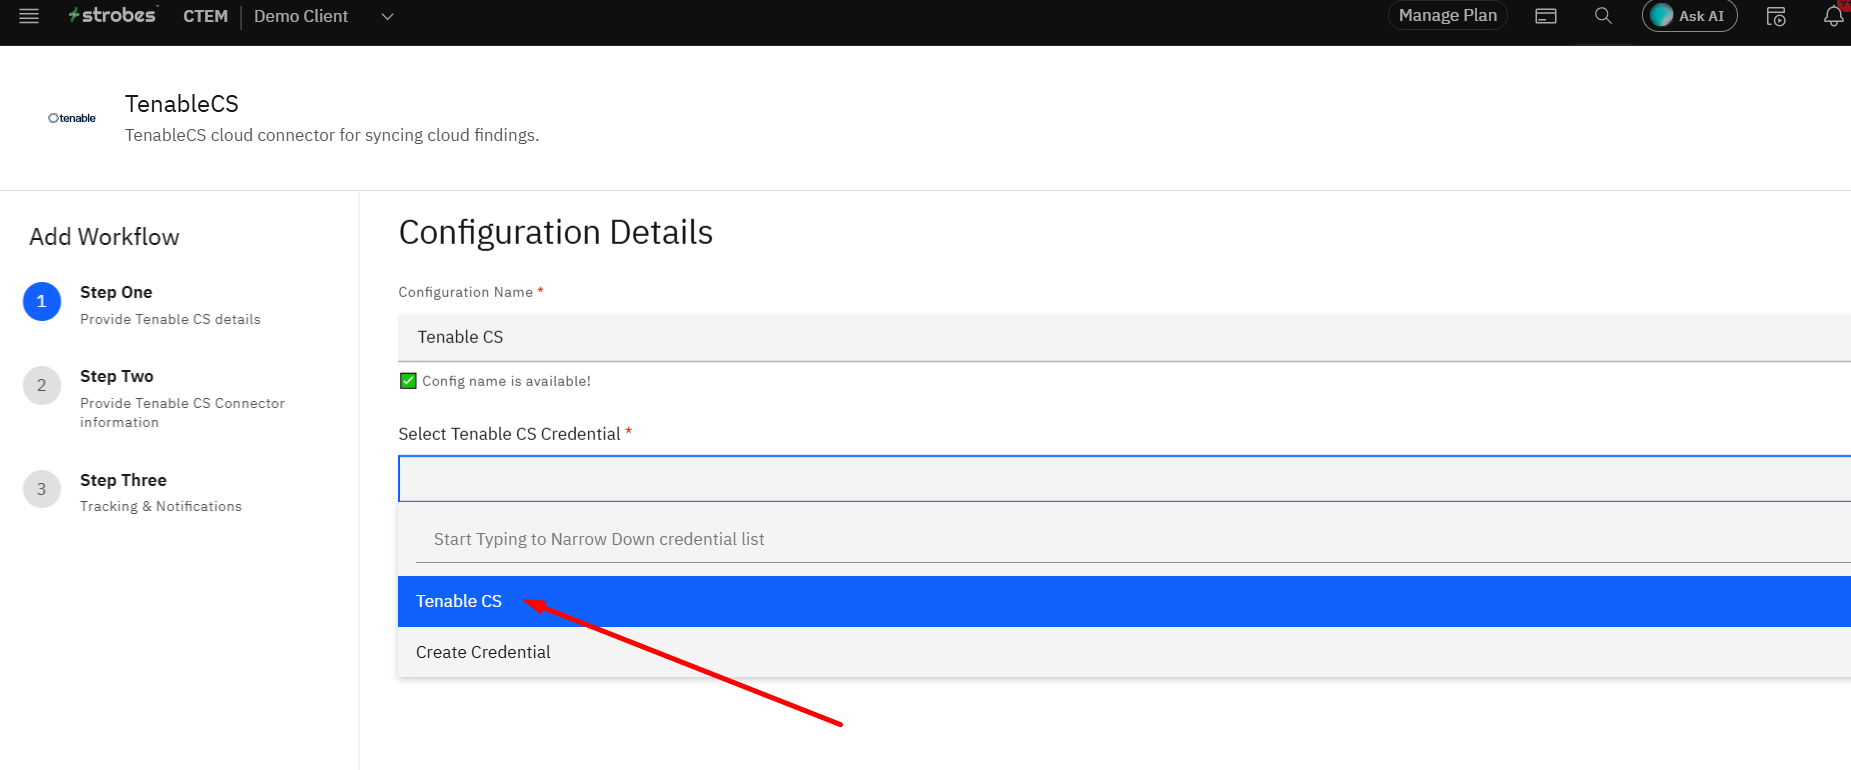
Step 6: Add a New Credential (if needed)
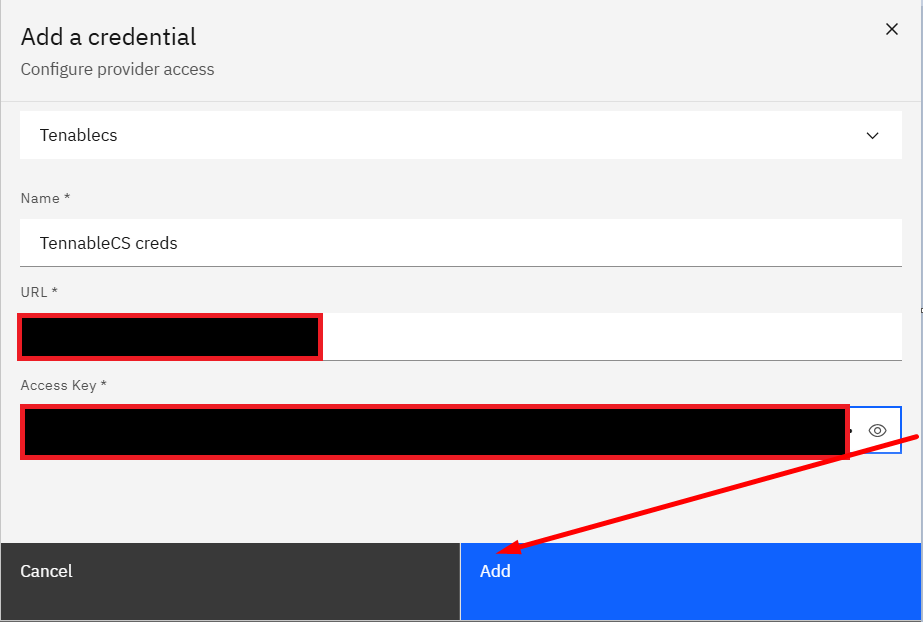
The Add a Credential modal opens. Fill in the following fields:
- Name (required) — Enter a label for this credential set, used for internal reference only.
- Base URL (required) — Enter your Tenable Cloud Security API Base URL.
- API Key (required) — Enter your Tenable CS API key.
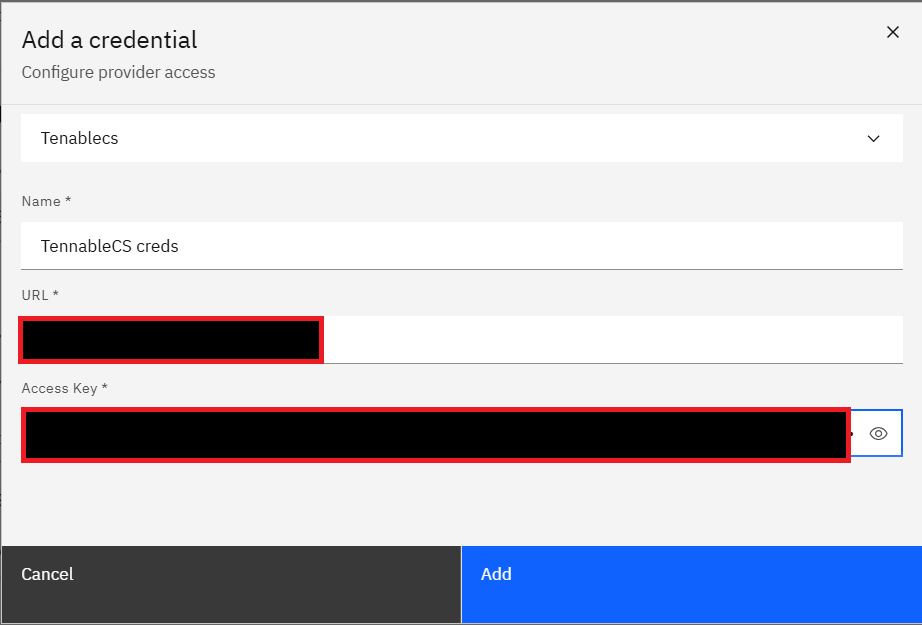
Step 7: Save the Credential
Click Add. The modal closes, and the newly created credential is automatically selected in the Configuration Details form.
Step 8: Choose a Baseline
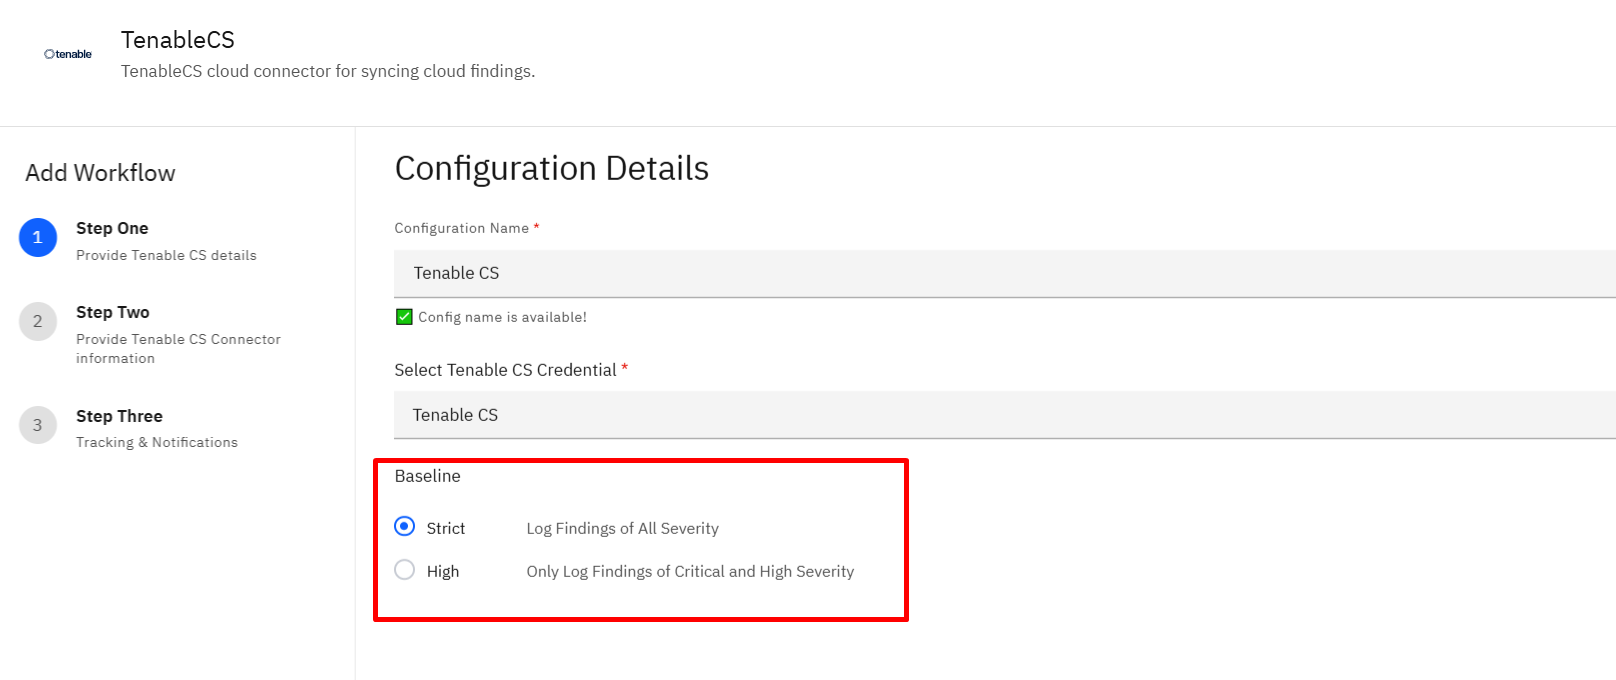
Under Baseline, select which findings to import from CrowdStrike:
Option | What it imports |
Strict | Findings of all severity levels |
High | Critical and High severity findings only |
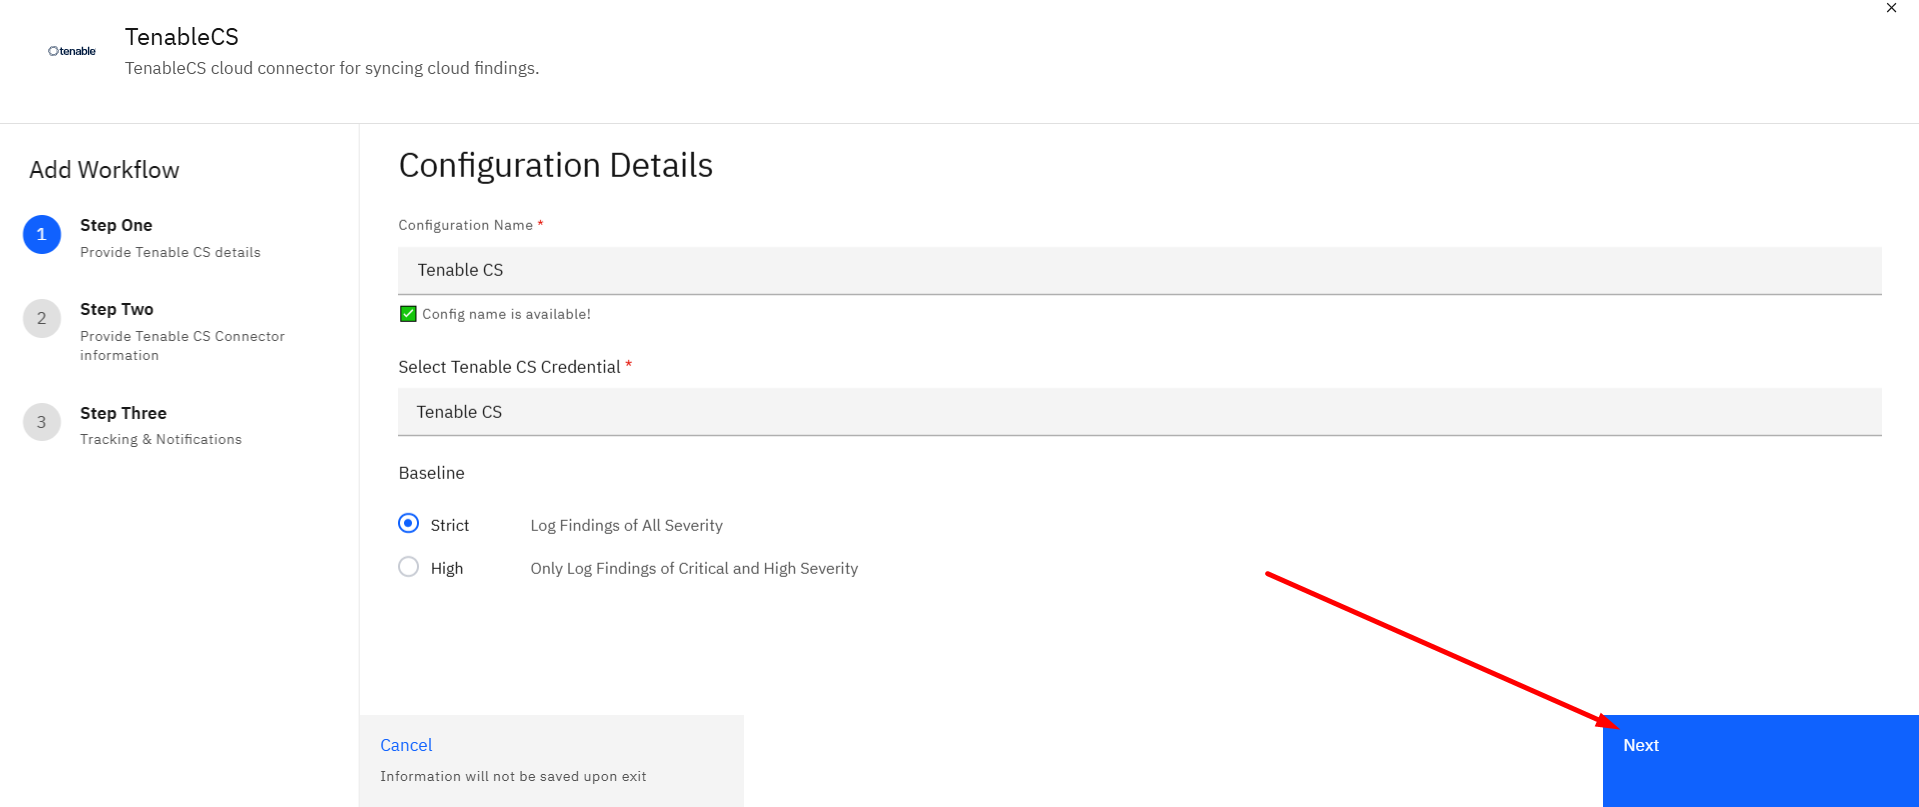
Step 9: Proceed to Step Two
Click Next to proceed to the next configuration step.
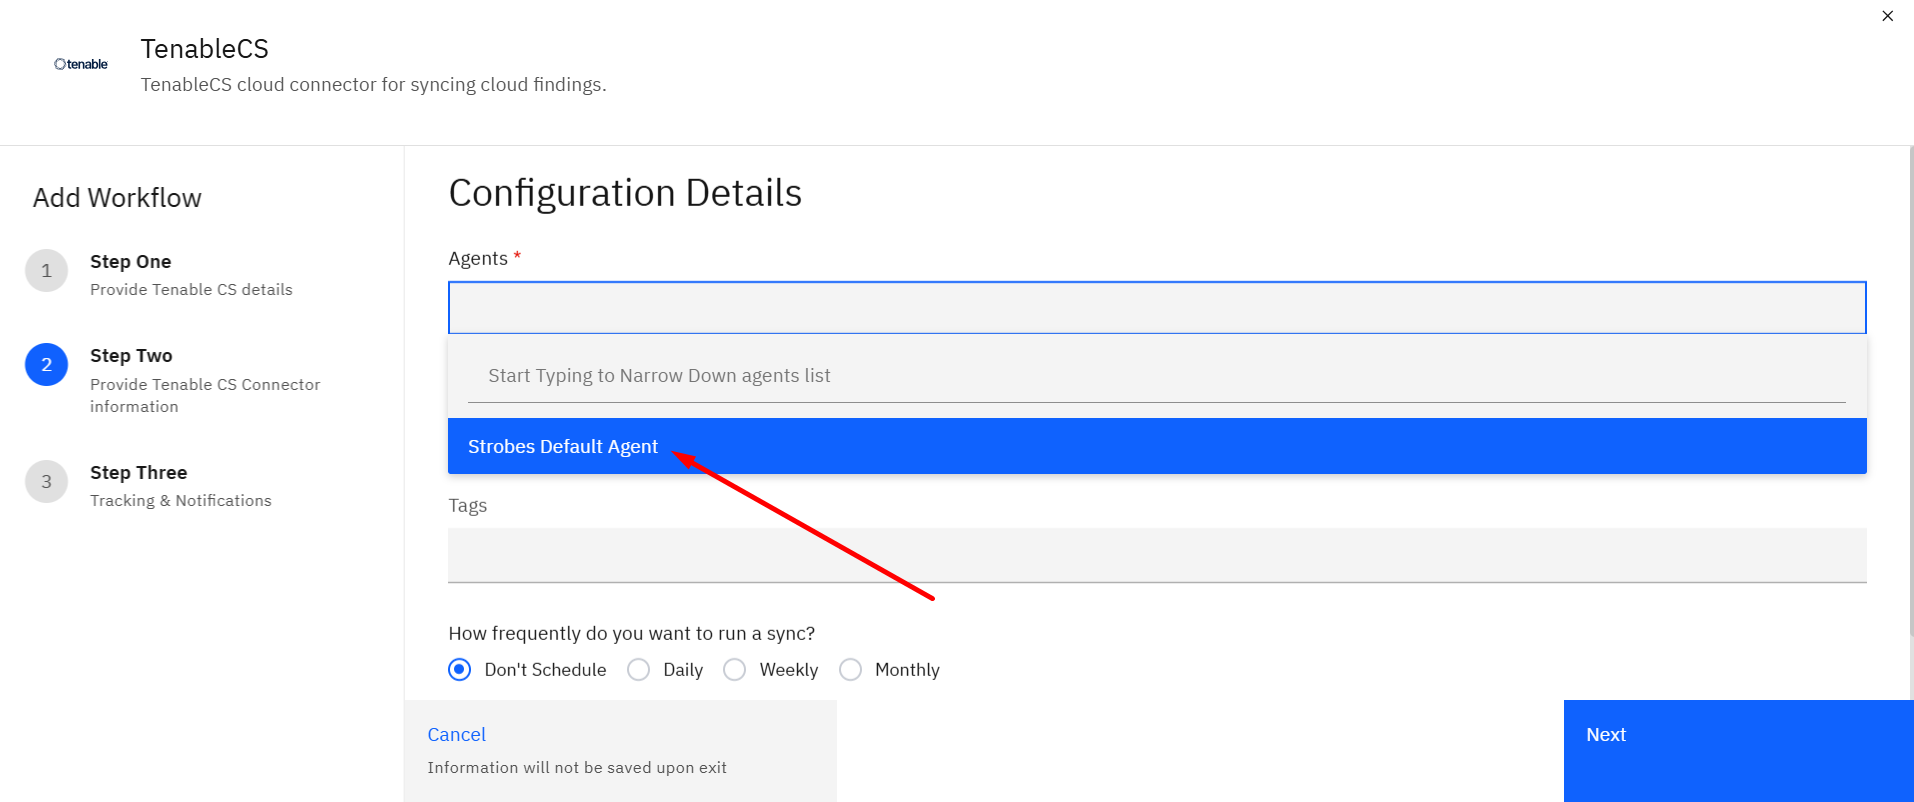
Step 10: Select an Agent
Click the Agents field and select the Strobes agent that will handle the connector's data. By default, Strobes Default Agent is selected.
Step 11: Add Account ID (Optional)
In the Account ID field, enter your Tenable Cloud Security account ID if required. This field is optional and can be left blank if not needed.
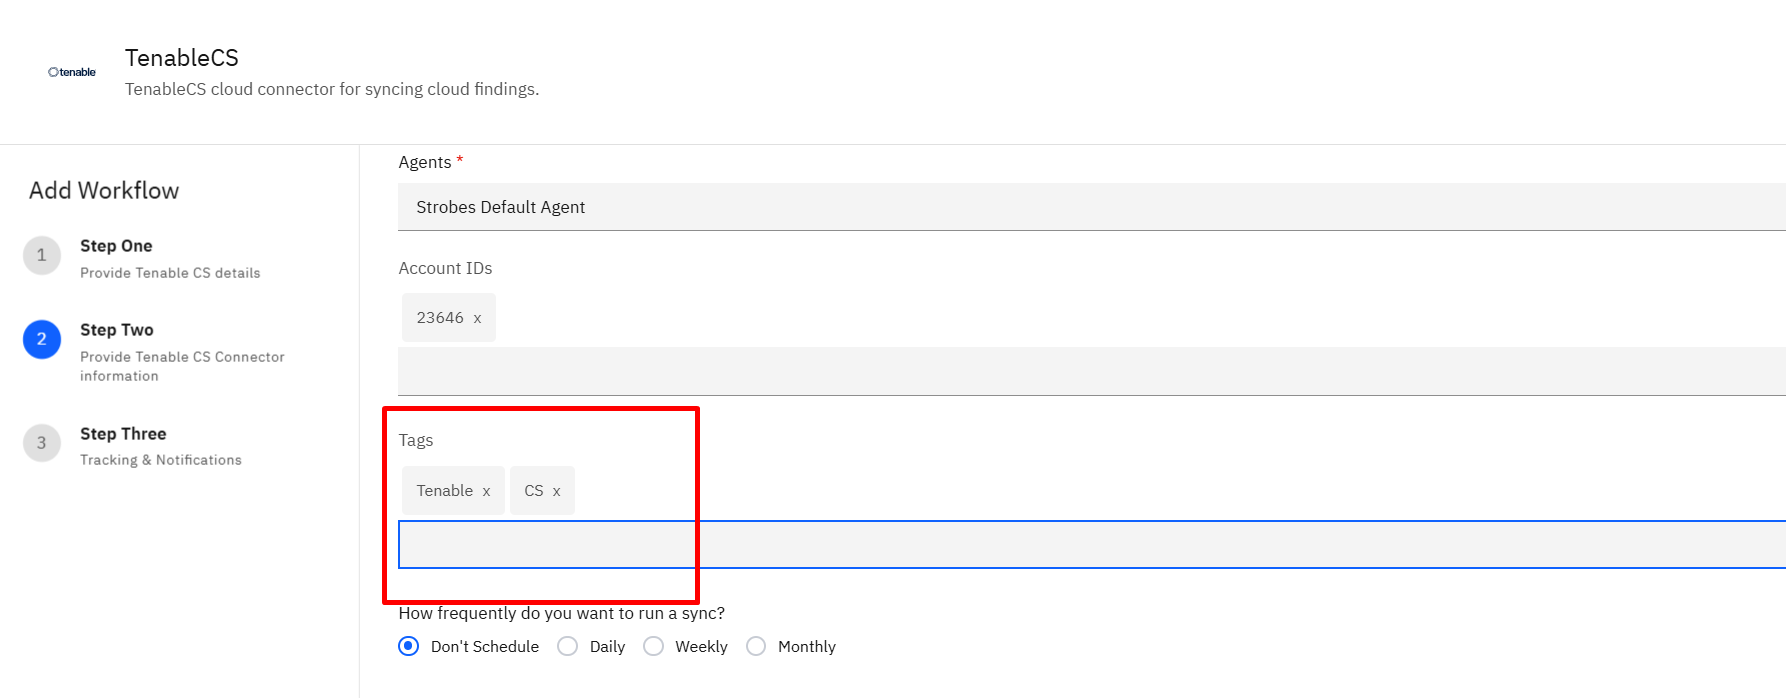
Step 12: Add Tags (Optional)
Click the Tags field and enter any tags you want to apply to the assets and findings imported by this connector. Tags help with filtering and scoping data within Strobes. Leave this field empty if no tags are needed.
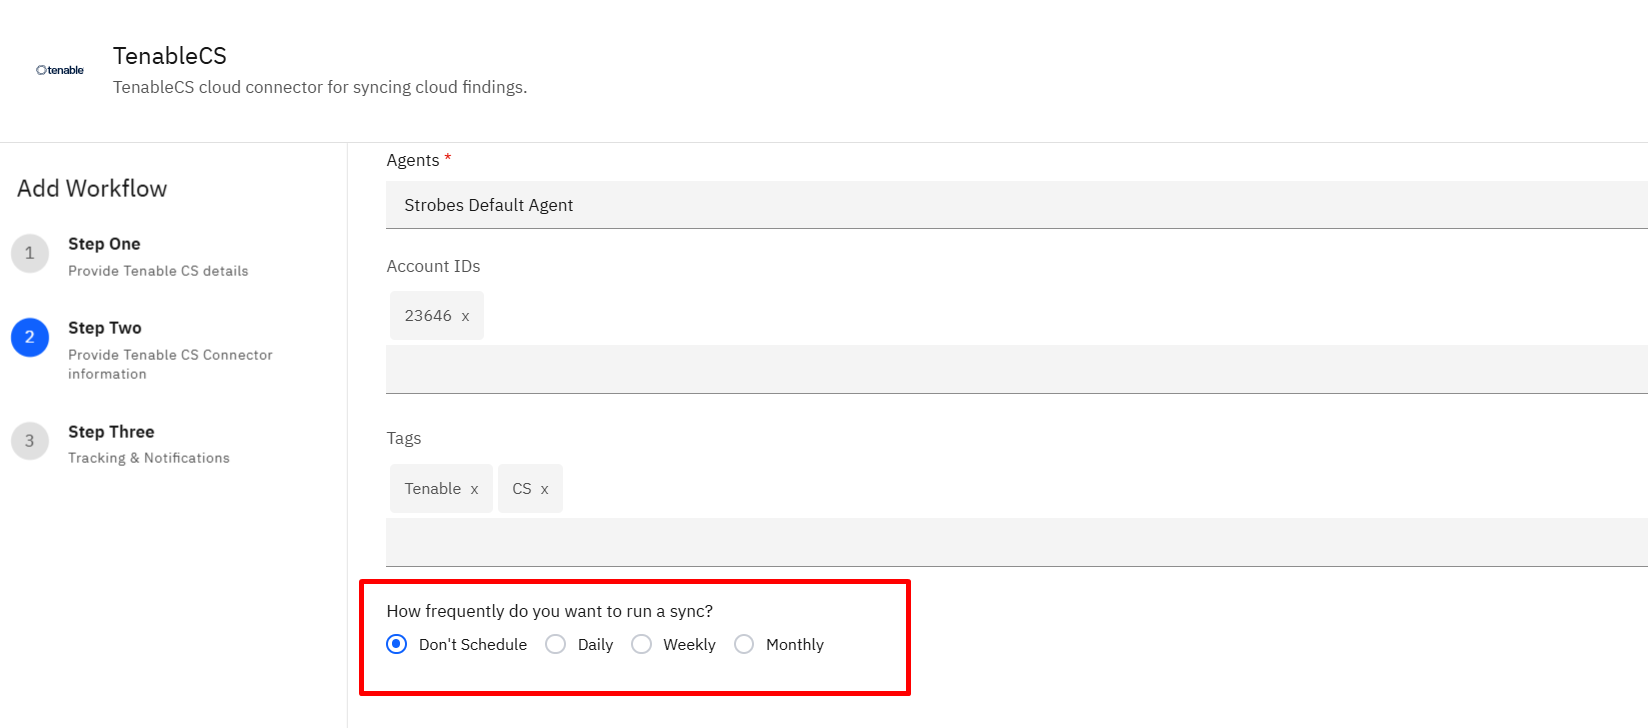
Step 13: Set Sync Frequency
Under How frequently do you want to run a sync?, select the desired recurring sync schedule for importing findings from Tenable CS into Strobes.
Option | Description |
Don't Schedule | Run syncs manually only |
Daily | Sync once every day |
Weekly | Sync once every week |
Monthly | Sync once every month |
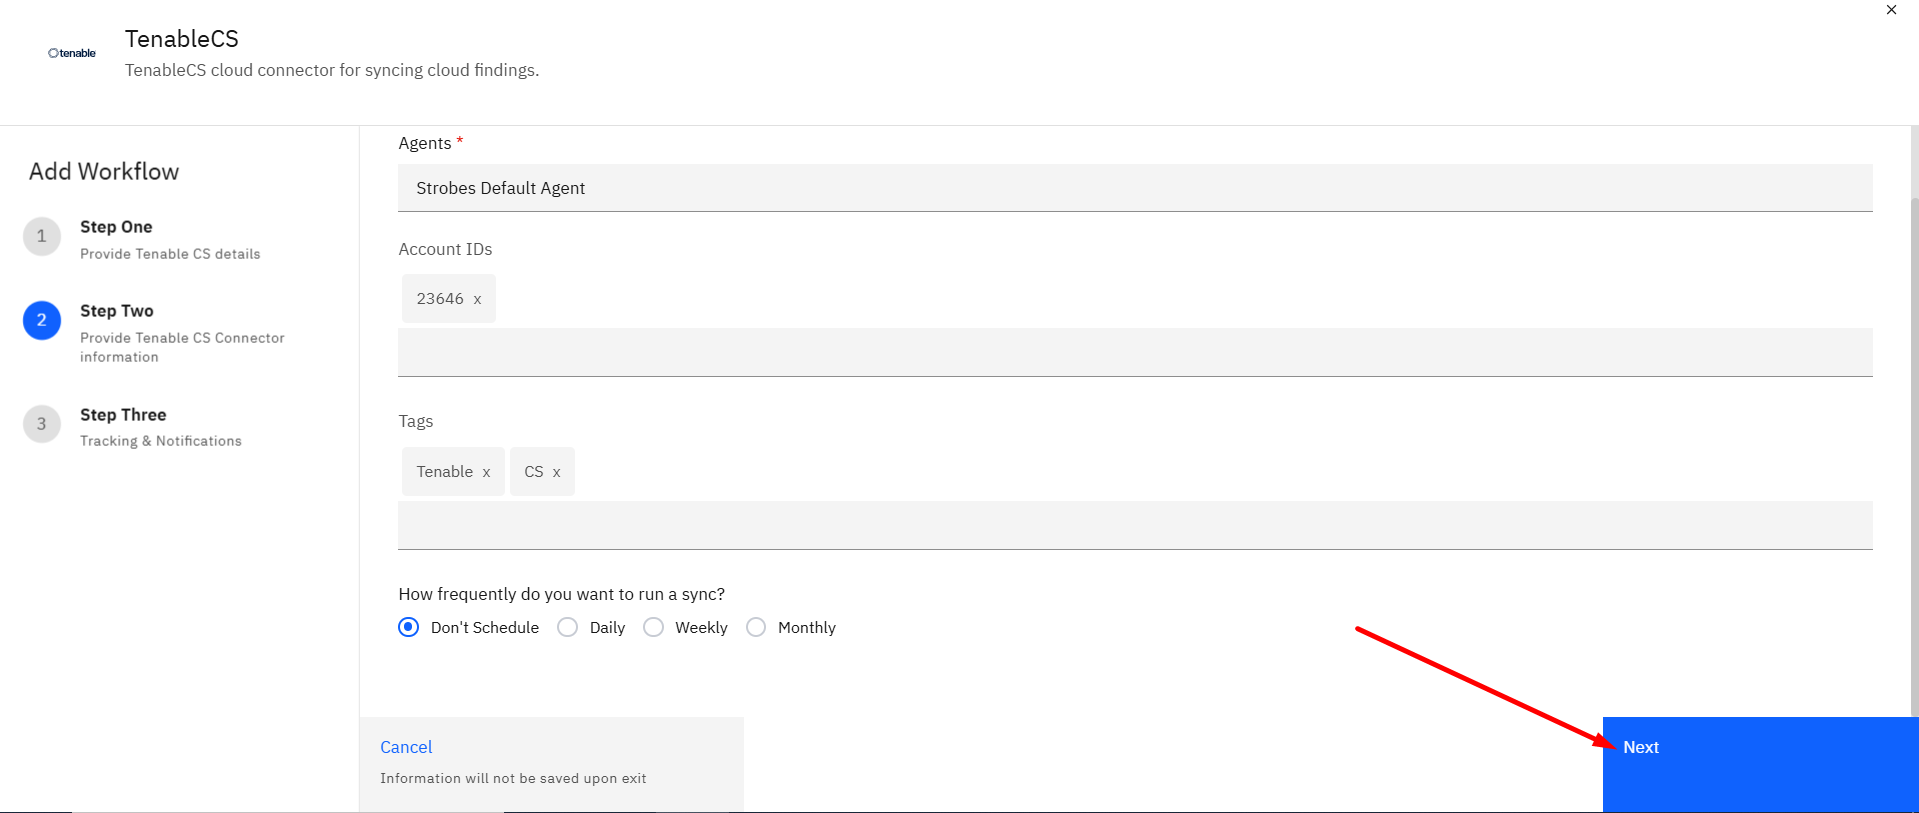
Step 14: Proceed to Step Three
Click Next to proceed to the third and final configuration step.
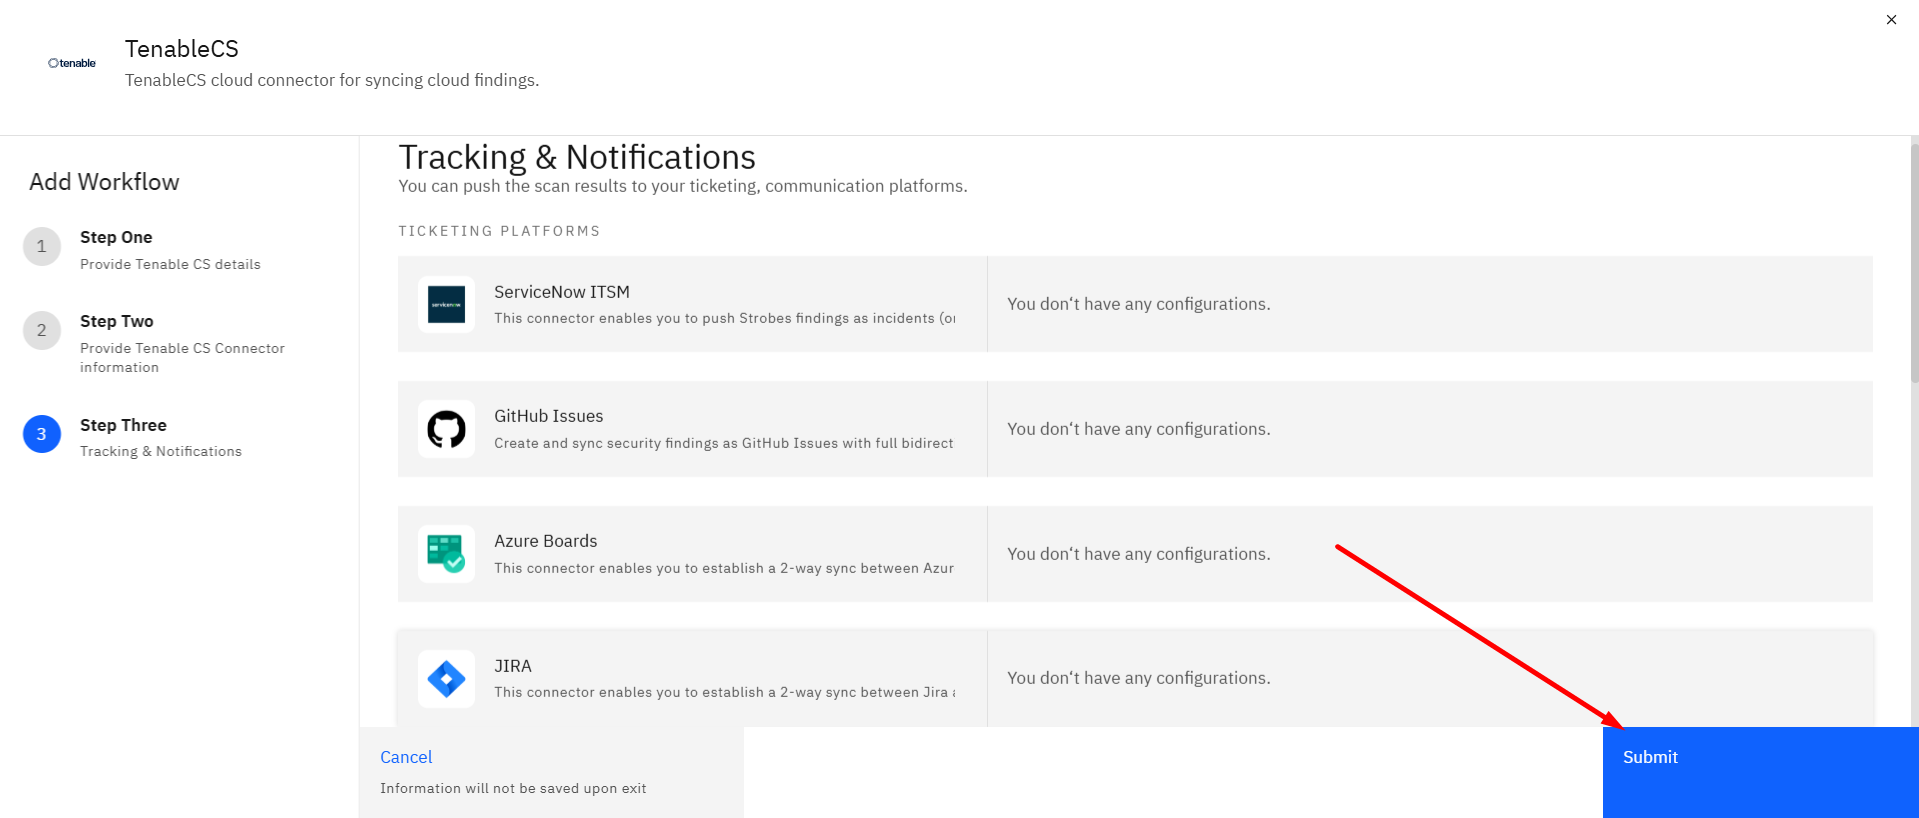
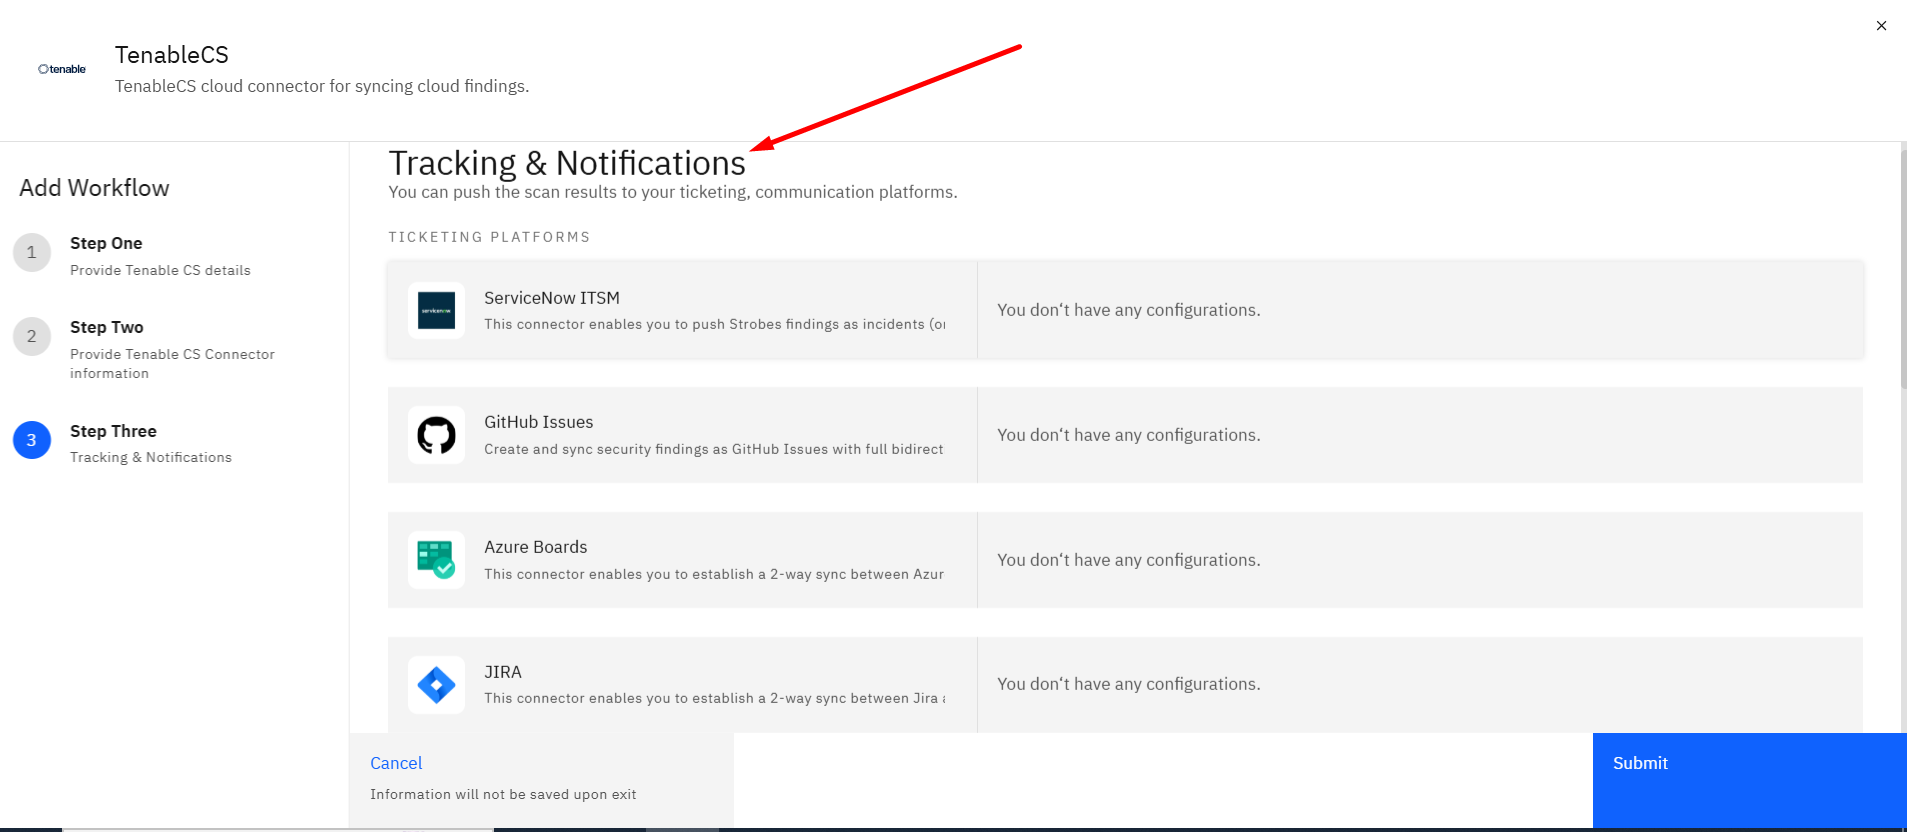
Step 15: Configure a Notification or Tracking Channel (Optional)
This step allows you to connect notification and tracking channels to the Tenable CS connector.
Notification Channels
You can configure a notification channel to receive updates when the connector syncs data or imports new findings. The available notification channels are:
- MS Teams
- Microsoft 365 Email
- Flock Messenger
- Slack
Tracking Tools
You can also connect tracking tools to receive imported findings as tickets for further tracking and remediation. The available tracking tools are:
- ServiceNow ITSM
- JIRA
- GitHub Issues
- Azure Boards
- Bugzilla – Strobes Sync Add-on
If a notification or tracking configuration is already available in Strobes, it will appear in the respective list and can be linked to this connector. If no configuration is available, you can skip this optional step and configure it later.
Step 16: Submit the Configuration
Click Submit to save and activate the connector. Strobes will begin syncing cloud security findings from Tenable CS according to the schedule you configured.